A GDPR risk assessment template XLS is a spreadsheet that records each personal-data processing activity, screens it against the nine high-risk criteria the European Data Protection Board uses, scores the likelihood and severity of harm to individuals, and tracks the measures that bring residual risk down. The free five-tab workbook below does all four.
On May 2, 2025, the Irish Data Protection Commission fined TikTok EUR 530 million for transferring European users’ data to China without verifying that Chinese law offered protection equivalent to the EU’s. EUR 485 million was for the transfer breach under Article 46 and EUR 45 million for a privacy notice that never named China.
Deputy Commissioner Graham Doyle said TikTok failed to verify, guarantee, and demonstrate that data accessed remotely by staff in China was protected. In February 2025 the company found that some EEA data had in fact been stored on Chinese servers, contrary to its evidence, and told the DPC in April.
|
GDPR Risk Assessment Template XLS: The Practitioner’s Cheat Sheet |
|
The download is a five-tab Excel workbook: Processing Register (Article 30 fields), DPIA Screening (the EDPB’s nine high-risk criteria with an automatic two-or-more flag), Scoring Scales, Risk Register (likelihood times severity with residual re-scoring), and Action Plan. |
|
Severity is scored on harm to the individual, never on cost to the organization. That is the GDPR test in Article 35 and the reason a generic IT risk matrix produces the wrong ranking. |
|
The Irish Data Protection Commission fined TikTok EUR 530 million on May 2, 2025 for transfers to China it had not verified as safe. The worked example in the template scores that exact risk before and after treatment. |
|
GDPR fines reached EUR 7.1 billion by January 10, 2026, with EUR 1.2 billion in 2025 alone, and breach notifications rose 22 percent to 443 a day (DLA Piper, January 2026). |
|
The EDPB adopted its first harmonised DPIA template on March 10, 2026 and published it April 14. After the June 9, 2026 consultation closes, national authorities align to it; the spreadsheet’s tabs map to its seven sections. |
|
Two or more Y answers on the screening tab means a DPIA is mandatory. A residual HIGH that cannot be reduced means prior consultation with the supervisory authority under Article 36. |
That is a risk assessment failure before it is a legal one. A transfer impact assessment row in a spreadsheet, scored honestly, would have shown a HIGH residual risk and forced a decision. The template on this page is built so that row exists, and the worked example uses TikTok’s facts.
What the GDPR Risk Assessment Template XLS Contains
The workbook follows the sequence the regulation itself sets. Article 30 requires a record of processing activities, Article 35 requires a data protection impact assessment where processing is likely to result in high risk, and Article 32 requires security measures appropriate to that risk. Each tab feeds the next.
Download the GDPR risk assessment template (XLSX, five tabs) and open the How to Use tab first. Blue cells are inputs, black cells calculate, and row 2 of every register is a worked example you replace with your own first entry. The file has no macros and opens in Excel, LibreOffice, and Google Sheets.
|
Tab |
What you enter |
What it calculates or enforces |
|
Processing Register |
One row per activity: purpose, lawful basis, data subjects, data categories, special categories, recipients, third-country transfers and mechanism, retention, DPO contact |
Drop-down for special categories; frozen reference column; the Article 30 record auditors ask for first |
|
DPIA Screening |
Y or N against nine EDPB criteria for each activity |
Counts the criteria met; flags DPIA REQUIRED at two or more; red highlight |
|
Scoring Scales |
Nothing; read it
|
Anchors for likelihood 1 to 5 and severity 1 to 5; HIGH 15 to 25, MEDIUM 6 to 14, LOW 1 to 5; severity floor of 3 for special-category and children’s data |
|
Risk Register |
Risk to the individual, cause, articles engaged, likelihood, severity, existing and additional measures, owner, date |
Inherent score and band; residual score and band after measures; traffic-light shading; status drop-down |
|
Action Plan |
Each additional measure with article, owner, due date, evidence |
Status tracking and a DPO sign-off column that closes the loop |
The structure differs from a generic risk matrix template in one way: the severity column asks about the person whose data it is. Recital 75 and Article 35 define the risk as one to the rights and freedoms of natural persons. A sheet that scores cost to the company ranks a EUR 530 million transfer risk below a website outage.
For readers who want the generic method behind the tabs, the complete risk assessment guide and the risk register guide cover scales, bands, and ownership. This page covers only what the GDPR adds to a risk register: the harm test, the screening criteria, the transfer question, and the sign-off the regulation expects a DPO to give.
Why the Spreadsheet Matters More After the 2025 Fines
The enforcement numbers behind any GDPR risk assessment template split in 2025: fines held level, breach notifications jumped. DLA Piper’s survey of January 2026 counted EUR 7.1 billion in GDPR fines since May 25, 2018, with EUR 1.2 billion issued in 2025. More than 60 percent of the total has been imposed since January 2023.
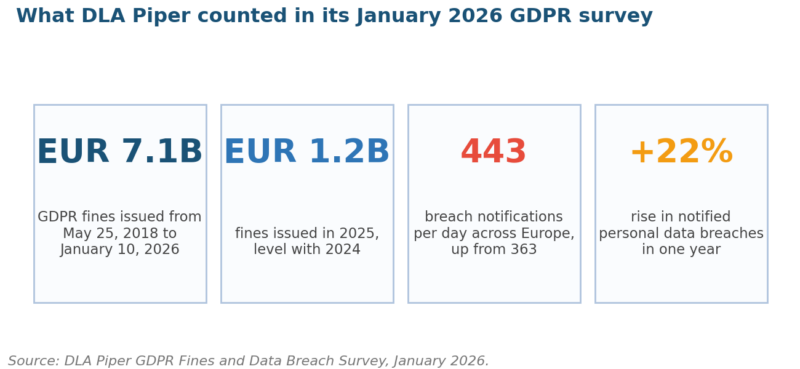
Figure 1. Cumulative fines, 2025 fines, and breach notifications from the DLA Piper survey of January 2026.
Breach notifications rose faster than fines. DLA Piper’s February 2026 analysis found an average of 443 notifications a day between January 28, 2025 and January 27, 2026, up 22 percent from 363 and the first year above 400 since the regulation began. Ross McKean, chair of the firm’s UK data practice, called the rise a sign of serious consequences.
|
Decision |
Date |
What the risk assessment missed |
Fine |
|
TikTok, Irish DPC |
May 2, 2025 |
No verified transfer impact assessment for remote access from China; notice did not name the destination country |
EUR 530M (EUR 485M Art 46; EUR 45M Art 13) |
|
Google, CNIL |
September 1, 2025 |
Advertising emails in Gmail tabs and account-creation cookies without valid consent |
EUR 325M |
|
LinkedIn, Irish DPC |
October 24, 2024 |
No valid lawful basis for behavioural analysis and targeted advertising |
EUR 310M |
|
Shein, CNIL |
September 1, 2025 |
Cookies placed on arrival and after reject-all; incomplete information |
EUR 150M |
Three of the four cases turn on a question the template asks in its first two tabs: what is the lawful basis, and where does the data go. CNIL’s Google decision and the LinkedIn decision are lawful-basis failures; TikTok is a transfer failure. None required new technology to detect.
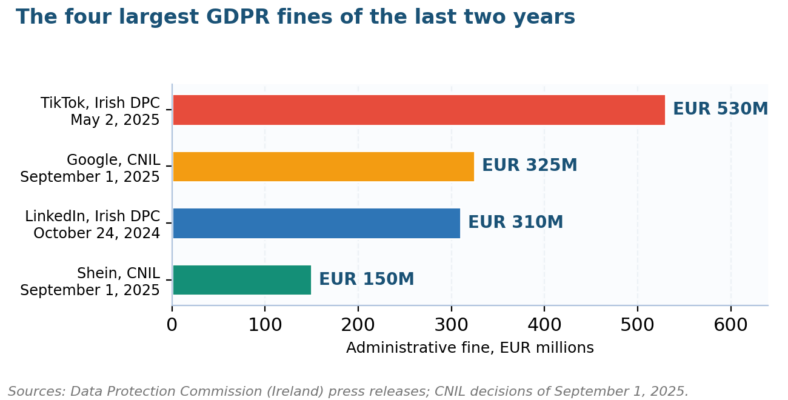
Figure 2. The four largest GDPR fines of the last two years, from the Irish DPC and CNIL decisions.
The concentration of enforcement in one regulator is the other reason to assess transfers carefully. The Irish DPC has issued EUR 4.04 billion of the EUR 7.1 billion total, because most US platforms have their EU establishment in Dublin. Privacy Laws & Business notes that the CNIL cookie fines were the largest in that authority’s history.
How to Run the Assessment From Processing Register to Action Plan
The tabs are ordered as a workflow, and the ICO’s DPIA guidance describes the same sequence in prose: describe the processing, assess necessity, identify risks, identify measures, sign off. The compliance risk assessment guide covers the organizational side; the six steps below are specific to personal data.
|
Step |
Action in the workbook |
GDPR anchor |
Time for a 15-activity organization |
|
1. Inventory processing |
Fill the Processing Register from system owners, contracts, and data flow diagrams; one row per purpose, not per system |
Article 30 |
Two to three days of interviews |
|
2. Screen for DPIA |
Mark Y or N on the nine criteria per activity; the sheet flags two or more |
Article 35(3); EDPB WP248 rev.01 |
Half a day |
|
3. Score inherent risk |
For each flagged activity, list risks to individuals; rate likelihood and severity 1 to 5 |
Recital 75; Article 35(7)(c) |
One day |
|
4. Record measures |
Existing controls, then additional measures under Articles 25 and 32; re-score residual |
Articles 25, 32, 35(7)(d) |
One day with security and legal |
|
5. Decide and consult |
Residual HIGH that cannot be reduced goes to the supervisory authority before processing |
Article 36 |
Eight weeks statutory response |
|
6. Track and review |
Action Plan with owner, date, evidence, DPO sign-off; re-screen on change and annually |
Article 35(11); Article 5(2) accountability |
Ongoing |
Step one is where the TikTok inquiry found the gap: staff in a third country could reach data the register did not show leaving Europe. Build the register by purpose and follow each purpose to every system and person that touches it. The risk identification guide describes the interview and document-review techniques.
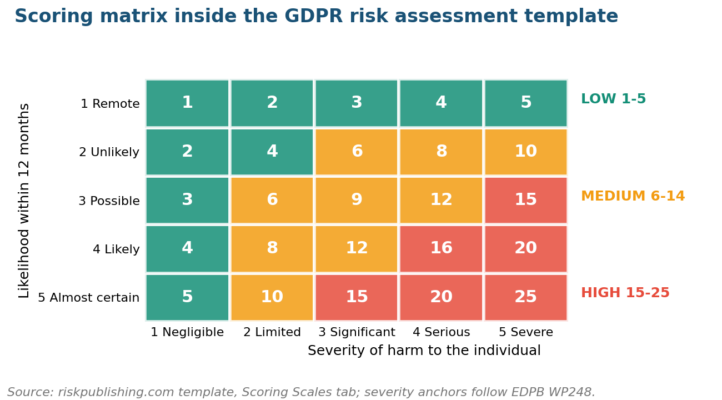
Figure 3. The scoring matrix in the Scoring Scales tab; severity anchors follow the harm categories in EDPB guideline WP248.
The matrix in Figure 3 does the scoring at step three. The severity anchors run from negligible inconvenience to physical harm, loss of liberty, or exposure of vulnerable people at scale, which is how the CNIL’s PIA method and the Irish DPC’s guide both describe harm. The template will not let special-category or children’s data score below 3.
At steps four and five, Article 25 on data protection by design and Article 32 on security enter the sheet. Pseudonymisation, encryption, access logging, and retention limits are the measures that move a score; a policy document on its own does not. Our risk controls guide separates preventive from detective measures.
The GDPR risk assessment template fills faster when the evidence is collected before the Processing Register is opened. The six items below each fill a column an auditor will check, and the TikTok inquiry turned on the third and fourth of them:
- Contracts and data processing agreements with every processor and sub-processor, including cloud regions
- Privacy notices as published, with the version date, so the register can be checked against what individuals were told
- System access lists showing which roles and locations can reach each data store
- Transfer mechanisms in force: adequacy decisions, standard contractual clauses, and any transfer impact assessments
- Retention schedules and the last deletion run for each system
- Breach and complaint logs for the past two years
Screening for a DPIA With the EDPB’s Nine Criteria
The DPIA Screening tab reproduces the nine criteria from the EDPB’s guidelines on high-risk processing, adopted from the Article 29 Working Party’s WP248 rev.01. The rule in the guideline is that processing meeting two or more criteria should be presumed to require a DPIA, and the sheet counts them for you.
|
Criterion |
What it covers |
Typical activity that meets it |
|
Evaluation or scoring |
Profiling and predicting, including behaviour, location, health, or interests |
Credit scoring; ad targeting on inferred interests |
|
Automated decisions with legal or similar effect |
Decisions with no human review that affect rights or access |
Automated loan refusal; automated hiring screen |
|
Systematic monitoring |
Observing or controlling people, including in public or at work |
CCTV analytics; employee productivity tracking |
|
Sensitive or highly personal data |
Article 9 and 10 data plus financial, location, and communications content |
Health apps; payroll; messaging platforms |
|
Large scale |
Volume of subjects, data, duration, or geographic reach |
National platform; multi-country HR system |
|
Matching or combining datasets |
Combining data from different sources beyond the subject’s expectation |
Loyalty data merged with third-party enrichment |
|
Vulnerable data subjects |
Children, employees, patients, asylum seekers, anyone with a power imbalance |
Ed-tech; workplace monitoring |
|
Innovative use or new technology |
New technology or novel application of existing technology |
Biometric access; generative AI on customer data |
|
Prevents exercise of a right or access to a service |
Processing that can exclude or deny |
Public-space screening; credit pre-checks |
National lists add to the nine. The ICO’s list of processing that always needs a DPIA in the UK and the Luxembourg CNPD decision under Article 35(4) are two examples, and the screening tab has a column to record which national item applies. The types of risk assessment guide places the DPIA among the others.
The EDPB’s own template changes the reporting format from June 2026. Adopted March 10 and published April 14, 2026, it runs seven sections from controllers and processors through the systematic description, necessity, risk assessment, and mitigation. Reed Smith notes it is not mandatory for controllers but will become the format authorities align to.
|
EDPB template section (April 2026) |
Workbook tab that feeds it |
Gap you fill outside the sheet |
|
1. Controllers, processors, sub-processors |
Processing Register, recipients column |
Contract references and DPA dates |
|
2. Technical sheet for the processing |
Processing Register, data and transfer columns |
Architecture diagram |
|
3. Systematic description |
Processing Register, purpose and lawful basis |
Narrative of the process |
|
4. Necessity and proportionality |
Not in the sheet |
Written justification per purpose |
|
5. Risk assessment |
Risk Register, inherent columns |
None |
|
6. Mitigation measures |
Risk Register residual columns; Action Plan |
None |
|
7. Sign-off and documentation |
Action Plan DPO sign-off column |
DPO advice and, where needed, Article 36 consultation record |
A Worked Example: Scoring a Third-Country Transfer
Row 2 of the Risk Register scores the TikTok scenario as the EDPB’s summary of the decision describes it: engineering staff in China accessing EEA user data, including data on minors, with standard contractual clauses signed but no transfer impact assessment that verified equivalent protection against Chinese surveillance and data-access laws.
|
Field |
Entry in the worked row |
Inherent (L x S) |
Additional measures (Art 25, 32, 46) |
Residual |
|
Risk to the individual |
EEA users’ data accessed from a jurisdiction whose laws allow state access without equivalent safeguards; users not told which countries their data goes to |
4 x 5 = 20 HIGH |
Documented transfer impact assessment; localisation of EEA accounts; supplementary technical measures; notice naming every third country; six-monthly access review |
2 x 5 = 10 MEDIUM |
|
Source or cause |
No TIA verifying essentially equivalent protection; privacy notice omits third-country names |
|
|
|
|
Articles engaged |
Art 46(1); Art 13(1)(f); Art 44 |
|
|
|
|
Screening result |
Criteria met: monitoring, large scale, matching, vulnerable subjects (4 of 9); DPIA required |
|
|
|
|
Owner and date |
Head of Privacy; December 31, 2026; status Open |
|
|
|
Severity stays at 5 after treatment because the harm, if it occurs, is unchanged: state access to a minor’s messages. Only likelihood falls, from 4 to 2, and the residual MEDIUM still needs DPO sign-off and a six-month review. That arithmetic is the point of separating the two axes.
The same row structure handles a SaaS vendor assessment, where the third country is the vendor’s support team, and an EU AI Act classification, where the innovative-technology criterion triggers the DPIA. The vendor questionnaire supplies the evidence for the recipients column.
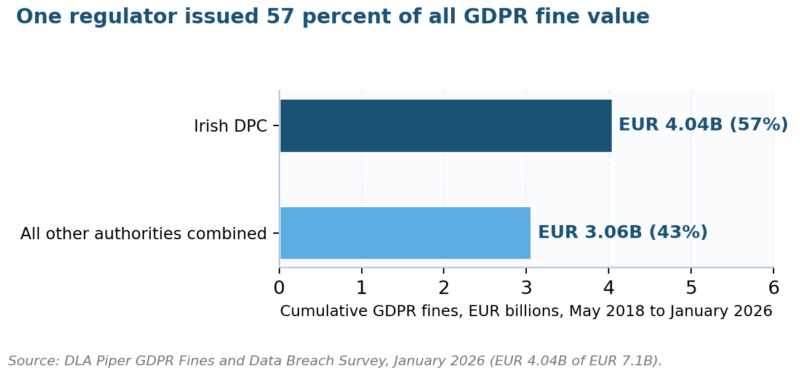
Figure 4. Cumulative GDPR fine value by authority, Irish DPC against all others, DLA Piper survey of January 2026.
Figure 4 explains why the transfer row scores so high on likelihood for any US-headquartered platform: the lead supervisory authority for most of them has issued 57 percent of all fine value. The Shein Ireland inquiry on this site follows a live cross-border case, and the data privacy KRIs give the indicators to watch between assessments.
Where GDPR Risk Assessment Templates Fail
The decisions above were issued against organizations with privacy teams, DPOs, and documented assessments. The table lists the failures the inquiries describe and the workbook feature or working practice that addresses each. The compliance risk management overview explains how a privacy register sits inside the wider obligations register.
|
Failure |
Where it appeared |
Fix in the template or the practice |
|
Register built per system rather than per purpose |
Remote access paths invisible because the system was in the EU |
One row per purpose; follow each purpose to every location that reads the data |
|
Severity scored on cost to the company |
Transfer risk ranked below operational risks |
Severity anchors are harm to the individual; special-category floor of 3 |
|
Screening skipped because the activity felt routine |
Advertising and cookie consent treated as marketing, not processing |
Every activity passes the nine criteria; two Ys is a DPIA regardless of opinion |
|
Measures recorded as policies rather than controls |
Contract clauses signed; no technical or verification step |
Additional measures must change likelihood or severity; residual re-scored |
|
No re-screen on change |
Storage location changed after the inquiry evidence was given |
Change triggers: new purpose, data category, technology, vendor, or country |
|
DPIA done, never signed off or revisited |
Assessment dated years before the decision |
DPO sign-off column; annual review date in the Action Plan |
|
Residual HIGH accepted silently |
No Article 36 consultation despite unresolved risk |
Scoring Scales tab makes consultation the required response for residual HIGH |
A spreadsheet is the right tool up to roughly 50 processing activities and two or three assessors. Beyond that, privacy management software or a compliance platform adds workflow and version control. The OneTrust and BigID comparison covers two of the common choices, and until then the workbook is enough and exports into any of them.
Standards outside the regulation help with the measures column of the GDPR risk assessment template. ISO/IEC 27701 extends ISO 27001 with privacy controls that map to Article 32, and the NIST Privacy Framework gives US organizations a structure that satisfies both GDPR and state privacy laws. The NIST CSF risk assessment guide shows how the two frameworks share a register.
GDPR Risk Assessment Template XLS: Your Questions Answered
Is a GDPR risk assessment template XLS the same as a DPIA?
No. The template is the working record; the DPIA is the assessment Article 35 requires for high-risk processing, and the EDPB template of April 2026 is the reporting format. This workbook produces the register, screening, scoring, and measures a DPIA needs, and the seven-section mapping above shows which parts you still write in prose.
When is a DPIA mandatory under Article 35?
Article 35(3) names three cases: systematic and extensive evaluation with legal or similar effect, large-scale processing of special-category or criminal data, and large-scale systematic monitoring of public areas. The EDPB adds that any processing meeting two or more of its nine criteria is presumed to need one, and national authorities publish further lists under Article 35(4).
How do you score risk in a GDPR risk assessment template XLS?
Rate likelihood of the harm event within 12 months from 1 to 5 and severity of harm to the individual from 1 to 5, multiply, then record measures and re-score. The template bands 15 to 25 as HIGH, 6 to 14 as MEDIUM, and 1 to 5 as LOW, with a severity floor of 3 for special-category data.
Does a US company need a GDPR risk assessment template?
Yes if it offers goods or services to people in the EU or monitors their behaviour, under Article 3(2), regardless of where it is established. The Irish DPC’s fines against US platforms show the exposure. The same workbook doubles as the record for state privacy laws, and compliance risk KRIs track both.
What is the penalty for not doing a required GDPR risk assessment?
Failing to carry out a DPIA falls under Article 83(4): up to EUR 10 million or 2 percent of worldwide annual turnover, whichever is higher. Breaches of the principles, lawful basis, or transfer rules fall under Article 83(5), up to EUR 20 million or 4 percent, the tier the TikTok and LinkedIn fines sit in.
How often should the GDPR risk assessment template be updated?
Re-screen and re-score whenever the purpose, data categories, technology, processors, or destination countries change, and review the whole register at least annually. Article 35(11) requires a review when the risk changes. TikTok’s evidence became inaccurate when storage locations changed, which is the kind of change a trigger list catches.
Can the GDPR risk assessment template XLS be used for UK GDPR?
Yes. The UK GDPR keeps Articles 30, 35, and 36 with the same numbering, and the ICO’s DPIA guidance and Article 35(4) list are the references to substitute. Add the ICO list items in the screening tab’s national-list column and use the ICO’s harm descriptions for the severity anchors.
Where GDPR Risk Assessment Is Heading After June 2026
The EDPB’s consultation on its DPIA template closed on June 9, 2026, and the consultation page holds the version national authorities will now align to. Expect regulators to ask for assessments in that seven-section shape from 2027 audits onward. The workbook maps to five of the seven sections; the necessity narrative and the sign-off record are written outside it.
Enforcement is also moving from headline fines to corrective orders with deadlines. TikTok received six months to bring transfers into compliance or suspend them, and CNIL attached a EUR 100,000 daily penalty to Google’s six-month deadline, as CNBC and the CNIL decision record. A residual score with an owner and a date is the document that answers a corrective order.
Screen every activity again before the end of 2026. Two changes justify it: the EU AI Act’s main obligations began applying on August 2, 2026 alongside the Commission’s data protection rules, and the DORA and NIS2 comparison shows how incident reporting now overlaps breach notification. The enforcement tracker shows what your own regulator fined last quarter.
If your organization has a processing register but no scored risks behind it, we populate the workbook with your team in two sessions and return it ready for DPO sign-off. Formats are on the services page, and the contact page opens the conversation. The download link is in the first section, and the TikTok row is already filled in.
Need the whole set?
The free file above stays free. The Risk Manager’s Toolkit bundles it with 39 other templates practitioners use: risk register, RCSA, business impact analysis with RTO and RPO, heat map, KRI scorecard, business continuity and disaster recovery plans, ISO 27001 and GDPR assessments. One download, Excel and Word, ready to edit.
Instant download after payment. 30-day refund, no questions. Secure checkout by Lemon Squeezy.
Chris Ekai is a Risk Management expert with over 10 years of experience in the field. He has a Master’s(MSc) degree in Risk Management from University of Portsmouth and is a CPA and Finance professional. He currently works as a Content Manager at Risk Publishing, writing about Enterprise Risk Management, Business Continuity Management and Project Management.