Compliance requirements are the obligations an organization must meet because a law, a regulation, a standard it has adopted, or a contract it has signed says so. Each requirement fixes what must be done, by whom, by when, and what evidence proves it. Miss one and the cost is a penalty, a lost contract, or a criminal resolution.
On July 17, 2026 the Department of Justice announced that The Scoular Company of Omaha, Nebraska would pay a $9,769,521 criminal penalty and forfeit $414,351 under a three-year deferred prosecution agreement. From 2013 to 2019 its employees had Mexican customs brokers pay more than $400,000 in bribes so that corn trains failing soil inspections could cross the border.
The company earned a 25% reduction from the bottom of the sentencing range for cooperation and remediation, and no credit for voluntary self-disclosure because it did not report the conduct in time. The requirement it broke, the Foreign Corrupt Practices Act, was one it already knew about. Knowing about compliance requirements and meeting them are different jobs.
| Compliance Requirements: The Practitioner’s Cheat Sheet |
| Compliance requirements are obligations imposed on an organization by a law, a regulation, a standard it has adopted, or a contract it has signed. Each one fixes what must be done, by whom, by when, and what evidence proves it was done. |
| The Scoular Company of Omaha agreed on July 17, 2026 to pay a $9,769,521 criminal penalty plus $414,351 in forfeiture under a three-year deferred prosecution agreement for FCPA bribery at the Mexican border; DOJ gave a 25% reduction for cooperation and none for self-disclosure. |
| Enforcement of compliance requirements is rising on the civil side too: False Claims Act recoveries hit a record $6.8 billion in FY2025, against $2.9 billion the year before, with 1,297 whistleblower suits filed. |
| Penalty scales for 2026 are published: HIPAA caps run from $36,505.50 to $2,190,294 per provision per year, OSHA serious violations stay at $16,550, and California’s largest CCPA penalty reached $12.75 million in May 2026. |
| Eight types of compliance requirements cover most organizations: government, industry, international, data privacy, contractual, governance, ethical and social, and quality. Every type produces line items in one obligations register. |
| The compliance requirements register feeds a program that prosecutors test with three questions from the DOJ Evaluation of Corporate Compliance Programs: is it well designed, is it resourced and empowered, and does it work in practice. |
| KPMG’s 2026 survey of 725 chief ethics and compliance officers found 77% investing in data analytics and 50% already using AI for compliance risk assessment; regulatory change was the top two-year challenge for 33%. |
The sections below cover where compliance requirements come from, the eight types most organizations face, and how to turn the list into an obligations register a prosecutor would accept. Our guides to compliance risk management and compliance management cover the discipline; this one covers the requirements.
What Compliance Requirements Are and Where They Come From
ISO 37301, the compliance management system standard, uses the term compliance obligations for requirements an organization must comply with and those it chooses to comply with. The ISO 37301:2021 text makes that split the foundation of the system: mandatory obligations from law and regulation, voluntary ones from standards, codes, and contracts. Both belong in the same register.
| Source | What creates the requirement | US examples | Evidence a regulator asks for |
| Law | A statute passed by Congress or a state legislature | FCPA, Sarbanes-Oxley, HIPAA, CCPA, OSH Act | Books and records, certifications, notices, training logs |
| Regulation | A rule an agency issues under a statute | 45 CFR Part 164 (HIPAA Security), 31 CFR Chapter X (BSA), 16 CFR Part 314 (FTC Safeguards) | Risk analyses, policies, transaction monitoring output, incident reports |
| Standard | A framework the organization adopts, or a customer requires | ISO 37301, ISO 27001, NIST CSF 2.0, COSO Internal Control, PCI DSS | Scope statement, control evidence, audit reports, certificates |
| Contract | A clause agreed with a customer, supplier, lender, or insurer | DFARS 252.204-7012 flow-downs, SLAs, data processing agreements, loan covenants | Attestations, audit rights exercised, covenant certificates |
The four sources of compliance requirements behave differently when they change. A statute changes rarely and visibly; a regulation changes through a notice-and-comment process you can track; a standard changes on a revision cycle; a contract changes whenever the counterparty renegotiates. The Competitive Enterprise Institute counted 1,255 federal rules by July 1, 2025, and every applicable one still entered the register.
Internal policies are the fifth source of compliance requirements that most lists omit. Once a board adopts a risk management policy or a code of conduct, the organization has created a requirement it can be held to by auditors, courts, and its own whistleblowers. The DOJ’s Evaluation of Corporate Compliance Programs asks whether the company follows its own policies.
A useful test for whether something belongs among your compliance requirements: can a third party with authority impose a consequence for missing it? If a regulator, a court, a certification body, or a counterparty can, it goes in the register. If only your own management can, it is a control standard, and it belongs in the control measure library.
Eight Types of Compliance Requirements With 2026 Penalties
The table below lists eight types of compliance requirements and attaches to each the governing text, the 2026 penalty scale, and the most recent enforcement example we could verify. The categories overlap in practice; a hospital’s HIPAA duty is government, industry, and data privacy at once.
| Type of compliance requirements | Governing text (US unless stated) | 2026 penalty scale | Verified 2026 example |
| 1. Government | OSH Act; tax, labor, environmental statutes | OSHA serious $16,550; wilful or repeat $165,514 per violation | OSHA memo of May 21, 2026 kept 2025 amounts because no October 2025 CPI was published |
| 2. Industry-specific | HIPAA (45 CFR 164); SOX 404; BSA/AML (31 CFR X) | HIPAA tier caps $36,505.50 to $2,190,294 per year | OSF Healthcare paid $552,250 on July 29, 2026 after a 2021 ransomware breach of 53,907 records |
| 3. International | FCPA; GDPR Art. 83; EU AI Act | GDPR up to 4% of global turnover; FCPA criminal fines under USSG Chapter 8 | Scoular DPA July 17, 2026: $9,769,521 penalty plus $414,351 forfeiture |
| 4. Data privacy | CCPA/CPRA; state privacy acts; FTC Safeguards Rule | CCPA $2,663 per violation, $7,988 intentional or involving minors | GM and OnStar $12.75 million on May 8, 2026, the largest CCPA penalty to date |
| 5. Contractual | DFARS, PCI DSS, SLAs, data processing agreements | Termination, damages, loss of card acceptance, audit costs | PlayOn Sports $1.10 million on March 3, 2026 for forcing tracking consent on school ticket buyers |
| 6. Corporate governance | Exchange listing rules; SEC disclosure rules; state corporate law | SEC civil penalties totalled $7.2 billion in FY2025 | SEC filed 456 actions in FY2025, with two-thirds of standalone cases charging individuals |
| 7. Ethical and social | UK Modern Slavery Act; UFLPA; supplier codes | Import detentions, contract loss, reputational damage | DOJ noted Scoular’s bribes ultimately benefited cartel operators, a factor it now weighs |
| 8. Quality | ISO 9001; FDA 21 CFR 820; ICH Q9(R1) | Warning letters, consent decrees, recalls | Quality requirements sit with the quality function but report into the same register |
Type 2 compliance requirements need the most attention in US healthcare because the penalty tiers changed on January 28, 2026. The inflation adjustment set the tier 1 cap at $36,505.50, tier 2 at $146,053, tier 3 at $365,052, and tier 4 at $2,190,294 per identical provision per calendar year. Culpability decides the tier; breach size decides where inside it the penalty lands.
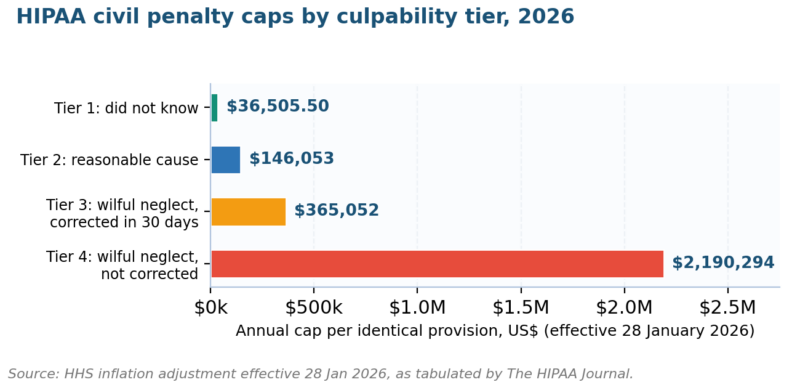
Figure 1. The tier 4 cap is sixty times the tier 1 cap. Correcting a wilful-neglect failure within 30 days drops the cap from $2.19 million to $365,052.
The OSF Healthcare resolution shows how one incident touches several types of compliance requirements. OCR found no accurate risk analysis under the Security Rule, an impermissible disclosure of 53,907 records, and late notices to individuals and to the Secretary. The fix is a two-year corrective action plan, and the starting point is the HIPAA risk assessment the rule already required.
Type 4 compliance requirements have moved fastest in 2026. California announced three penalties in four months: Disney for $2.75 million on February 11 for opt-out failures across streaming devices, PlayOn Sports for $1.10 million on March 3, and General Motors and OnStar for $12.75 million on May 8 for selling driving and location data from hundreds of thousands of drivers without consent.
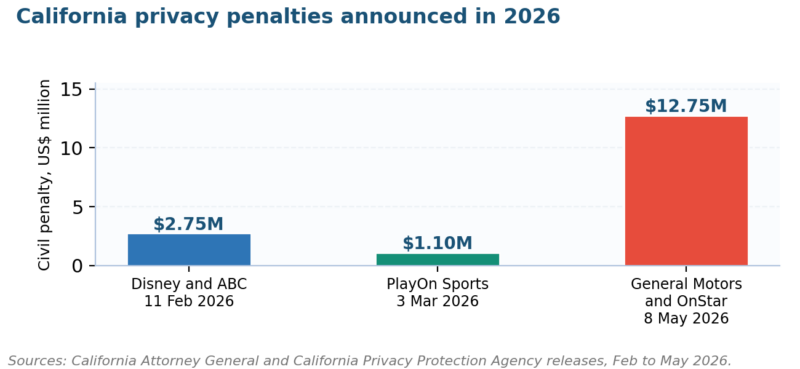
Figure 2. Three California privacy penalties in 2026 for data privacy compliance requirements. The GM settlement also bans sales of driving data to consumer reporting agencies for five years.
The PlayOn Sports decision is the one mid-sized firms should study. The company forced users of its GoFan school ticket platform to accept tracking before showing tickets and sent opt-outs to industry websites in place of its own mechanism. Our GDPR risk assessment template maps the same controls for EU data under Article 83.
Why the Requirements Matter: The 2025 to 2026 Enforcement Record
The argument for treating compliance requirements as a managed portfolio rests on numbers published in the last nine months. On January 16, 2026 the Department of Justice reported False Claims Act settlements and judgments above $6.8 billion for the fiscal year ending September 30, 2025, the highest in the statute’s history and more than double the prior year’s $2.9 billion.
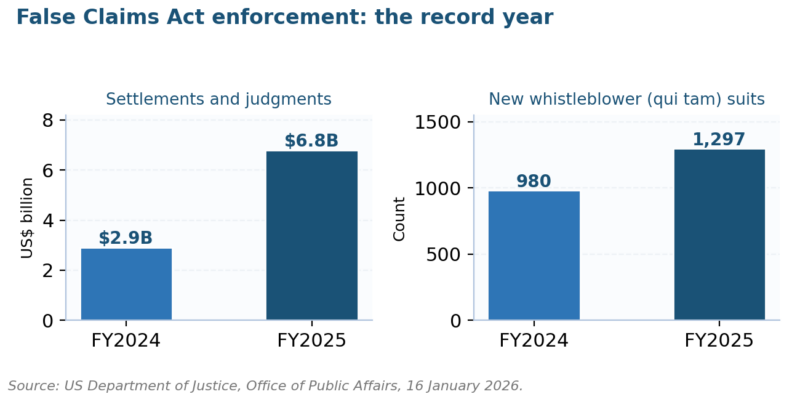
Figure 3. Compliance requirements enforced: whistleblowers filed 1,297 qui tam suits in FY2025, up from 980. Health care accounted for $5.7 billion of the $6.8 billion recovered.
Two facts in that release matter more than the headline. Whistleblowers filed 1,297 qui tam suits, up from the previous record of 980, and the government opened 401 of its own investigations. Roughly 84% of recoveries came from health care, so any organization billing Medicare or Medicaid should treat billing accuracy as one of its top-tier compliance requirements, with a named owner.
Securities enforcement moved the other way in volume and the same way in emphasis. The SEC’s fiscal 2025 results, analysed by Sidley on the Harvard corporate governance forum, show 456 actions against 583 the year before, but two-thirds of standalone cases charged individuals, a 27% rise. Tips, complaints, and referrals reached a record 53,753: fewer cases, more people named.
| Regulator or statute | FY2024 or prior | FY2025 or 2026 | What it means for your compliance requirements |
| False Claims Act recoveries | $2.9 billion | $6.8 billion | Federal billing and grant conditions are top-tier requirements |
| Qui tam suits filed | 980 | 1,297 | Internal reporting channels must beat the whistleblower to the regulator |
| SEC enforcement actions | 583 | 456 | Volume down, individual accountability up 27% |
| SEC tips, complaints, referrals | About 45,000 | 53,753 (record) | Assume every gap is reportable by someone |
| GDPR fines recorded by CMS | EUR 5.6 billion | EUR 6.11 billion across 2,685 fines to March 1, 2026 | EU data requirements now carry a decade of precedent |
| OCC BSA/AML orders | Ongoing | Community Federal Savings Bank (May 2026), United Texas Bank (July 2026) | Program deficiencies alone trigger orders, before any laundering is proved |
The OCC’s July 2026 enforcement list includes a cease and desist order against United Texas Bank of Dallas for weaknesses in its Bank Secrecy Act program that resulted in violations of law. The order names the program rather than a laundering event, and under the Basel Committee’s 2005 compliance principles the function itself is the requirement.
Outside the United States the pattern for compliance requirements holds. The CMS GDPR Enforcement Tracker recorded 2,685 fines worth EUR 6.11 billion by March 1, 2026, up 440 fines and EUR 487.6 million on the prior edition, with insufficient legal basis and insufficient security measures the most common grounds. Both are requirement failures a compliance risk analysis would have ranked high.
How to Build the Obligations Register
The register converts compliance requirements into work. ISO 37301 clause 4.5 requires an organization to identify its obligations and evaluate their impact, and the US Sentencing Guidelines, Chapter 8, make a documented compliance and ethics program the basis for a reduced culpability score. Neither text says what the register looks like; the worked example below fills that gap.
Each line in the register carries the same eight fields, whatever source the compliance requirements come from. The fields are fixed so that lines from a statute, a contract, and a standard can be sorted, filtered, and scored together, and so that an auditor or a new owner can read any line without a briefing.
- Requirement, quoted or cited to the clause, section, or contract paragraph, never paraphrased from memory.
- Source type: law, regulation, standard, contract, or internal policy.
- Owner by role, with a named deputy, and the business unit where the obligation is performed.
- Frequency and next due date for the action, the report, or the certification.
- Evidence that proves performance, stored where an auditor can retrieve it without asking the owner.
- Inherent likelihood and impact of a breach, scored on the same scale the enterprise risk register uses.
- Controls that reduce the risk, cross-referenced to the control library.
- Residual rating and the escalation trigger that sends a miss to the compliance committee.
| Requirement (cite) | Source | Owner | Frequency / evidence | Rating and trigger |
| HIPAA Security Rule risk analysis, 45 CFR 164.308(a)(1)(ii)(A) | Regulation | CISO; deputy privacy officer | Annual and on material change; signed analysis and risk management plan | L4 x I4 = 16; trigger: analysis older than 12 months |
| CCPA opt-out of sale or sharing, Cal. Civ. Code 1798.120 and 1798.135 | Law | Head of digital; deputy general counsel | Continuous; monthly test of the opt-out link and GPC signal | L3 x I4 = 12; trigger: any failed monthly test |
| FCPA anti-bribery, 15 U.S.C. 78dd-1; third-party due diligence | Law | Chief compliance officer; regional finance director | Before onboarding and every two years; due diligence file and payment review | L2 x I5 = 10; trigger: any facilitation or reinspection payment |
| SOX 404 internal control over financial reporting, PCAOB AS 2201 | Law and standard | Controller; head of internal audit | Annual; management assessment and auditor attestation | L2 x I4 = 8; trigger: any deficiency rated significant |
| Customer DPA clause 9: breach notice within 48 hours | Contract | Head of security operations; account director | Per incident; incident log with timestamps | L3 x I3 = 9; trigger: any incident open past 24 hours |
| FTC Safeguards Rule, 16 CFR 314.4(c): access controls and encryption | Regulation | CISO; IT operations manager | Continuous; quarterly access review and encryption inventory | L3 x I3 = 9; trigger: unencrypted customer data found |
Three choices in that table are deliberate: the citation column quotes the clause so a new owner can read the requirement without a lawyer. The owner is a role with a deputy, because Scoular’s scheme ran six years with nobody owning the customs broker relationship. The trigger is objective, so escalation does not depend on judgment under pressure.
Scoring uses the enterprise scale on purpose. A compliance risk assessment that runs on its own scale cannot be compared with operational or cyber risk at the board, and the register loses budget arguments it should win. Our guide on what compliance risk is explains why likelihood is usually the component practitioners under-score.
For projects and change programs the compliance requirements register is duplicated at project level with the same fields, then rolled up. The project manager’s role in compliance risk management is to own that project register, because a data residency clause or a DFARS flow-down is breached inside a project long before the enterprise function sees it.
How to Turn the Register Into a Compliance Program
A register is evidence of knowledge; a program is evidence of action, and prosecutors test action. The DOJ Evaluation of Corporate Compliance Programs, updated in September 2024, asks three questions: is the program well designed, is it resourced and empowered to function, and does it work in practice. Every element below answers one of them.
| Program element | DOJ ECCP question it answers | ISO 37301 clause | Minimum evidence |
| Risk assessment tied to the register | Well designed | 4.6 and 6.1 | Register with ratings, refreshed annually and on trigger |
| Policies and procedures | Well designed | 5.2 and 7.5 | Version-controlled documents mapped to requirements |
| Training and communication | Well designed | 7.2 and 7.3 | Completion by role, tested comprehension, refreshers on change |
| Confidential reporting and investigation | Works in practice | 8.3 and 8.4 | Hotline statistics, case files, time to close, retaliation checks |
| Third-party management | Well designed | 8.1 | Due diligence files, contract clauses, ongoing monitoring |
| Resources, autonomy, and data access | Resourced and empowered | 5.1, 5.3, 7.1 | Budget, reporting line to the board, access to transaction data |
| Monitoring, testing, and continuous improvement | Works in practice | 9.1 to 10.2 | Testing results, root-cause records, closed corrective actions |
| Incentives and discipline | Works in practice | 5.3 and 7.2 | Compensation clawbacks, consistent sanctions across grades |
Resourcing is where programs fail the second question. The 2024 ECCP update asked whether compliance has access to the same data the business uses, and whether the business’s AI tools are under compliance oversight. In KPMG’s 2026 survey of 725 compliance officers, 77% named data analytics a primary investment driver and 50% use AI for compliance risk assessment.
A training needs assessment run against the register shows whether the people who face each risk were trained on it, which is the evidence the DOJ asks for.
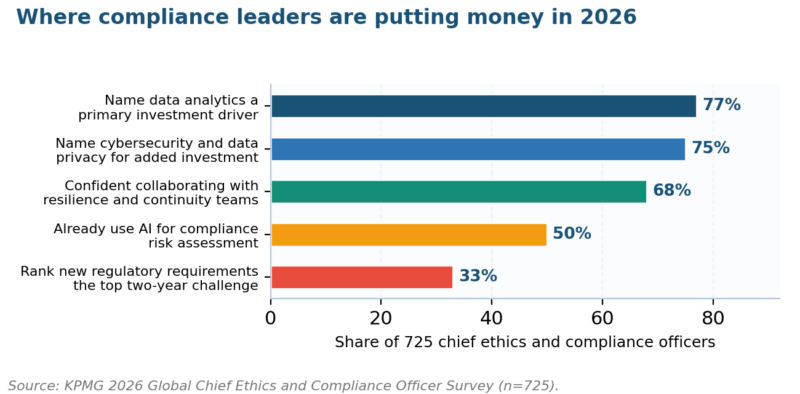
Figure 4. One in three compliance leaders ranks new compliance requirements as the top challenge of the next two years; three in four are buying analytics and privacy capability to meet it.
Ownership matters as much as the elements. Under the IIA Three Lines Model, the business owns the requirement and performs it, the compliance function designs the framework and monitors, and internal audit gives independent assurance. Our explainer on the three lines of defense covers the hand-offs, and a compliance officer who performs a control cannot then monitor it.
For information security compliance requirements the program borrows its structure from NIST Cybersecurity Framework 2.0, whose Govern function was added in 2024 to hold exactly this kind of obligation mapping. The cybersecurity risk management guide shows how the CSF functions line up with HIPAA, the FTC Safeguards Rule, and state rules such as the NYDFS cybersecurity regulation.
Financial reporting compliance requirements need their own line because the evidence standard is set by an external auditor. PCAOB AS 2201 defines what an integrated audit of internal control over financial reporting tests, and COSO’s Internal Control framework is the criteria almost every US filer adopts. Map the SOX 404 register lines to COSO components and the auditor’s questions become predictable.
Monitoring, Reporting, and Keeping Up With Change
Monitoring answers the third DOJ question: does the program work in practice? A monitoring plan states, for each of the compliance requirements in the register, who tests it, how often, with what sample, and what result triggers escalation. The tests feed a small set of indicators the compliance committee sees every quarter.
| Indicator | How it is measured | Amber / red threshold | Why it predicts a breach of compliance requirements |
| Register lines past due | Count of actions or certifications overdue at month end | Amber 1, red 3 or any top-tier line | Overdue lines were the pattern in the OSF and United Texas Bank orders |
| Control test failure rate | Failed tests divided by tests run, by requirement type | Amber 5%, red 10% | Failures cluster before incidents, as in repeated AML monitoring gaps |
| Hotline reports per 1,000 staff and median days to close | Case system extract | Amber under 0.5 reports or over 45 days; red under 0.3 or over 60 | Silence usually means fear; the FY2025 qui tam record shows where reports go instead |
| Training completion by high-risk role | LMS completion for roles named in the register | Amber 95%, red 90% | DOJ credits training targeted at the people who face the risk |
| Regulatory changes not yet assessed | Change log entries older than 30 days without an impact note | Amber 3, red 5 | 33% of CCOs rank new requirements their top challenge; unassessed change is the leading indicator |
| Third parties past due for renewed diligence | Vendor master compared with diligence dates | Amber 2%, red 5% | Customs brokers ran Scoular’s bribery scheme for six years unreviewed |
The thresholds above are starting points and should be tuned against your own history. Our key risk indicators examples article explains how to set them from data, and the risk management KPI dashboard guide covers presentation to a board that has fifteen minutes for the topic.
Keeping up with change in compliance requirements is a process with three inputs, and each input should have a named owner. The inputs run on different clocks, so one person watching all three will miss the fastest one, which in most organizations is the contract clause.
- Regulatory horizon scanning: Federal Register and state register subscriptions filtered to the CFR parts and codes in the register, reviewed weekly, with an impact note within 30 days.
- Standard revision tracking: certification body notices for every ISO, NIST, or PCI standard adopted, with transition deadlines entered as register lines.
- Contract change control: a legal review step that flags any new compliance clause in a signed agreement to the register owner within five working days.
One change shows why scanning cannot be annual. The EU’s Digital Omnibus on AI, Regulation (EU) 2026/1744, entered into force on July 27, 2026 and moved Annex III high-risk obligations to December 2, 2027, while Article 50 transparency duties applied from August 2, 2026 as planned. A register refreshed only in January would carry both dates wrong.
Reporting on compliance requirements is the last step. The compliance committee receives the indicator table quarterly; the board receives the chief compliance officer’s annual attestation, the register’s top ten lines by residual rating, and every red indicator with its corrective action. That is the cadence our risk-based internal audit guide recommends, and the incident management process guide covers the 48-hour breach clock.
Technology helps only after the compliance requirements register exists. Platforms compared in our OneTrust versus BigID review automate horizon scanning, evidence collection, and test scheduling, and none of them can decide which requirements apply to you. The GRC framework guide sets out the sequence: register, then process, then tool.
Compliance Requirements: Your Questions Answered
What are compliance requirements in simple terms?
Compliance requirements are the things an organization must do or avoid because a law, a regulation, an adopted standard, or a signed contract says so. Each one has an owner, a deadline or frequency, and evidence that proves it was met. Missing one brings a consequence from outside management: a fine, an order, a lost contract, or a prosecution.
What are the main types of compliance requirements?
Eight types cover most organizations: government, industry-specific, international, data privacy, contractual, corporate governance, ethical and social, and quality. The types overlap, so a hospital’s HIPAA risk analysis is a government, industry, and privacy requirement at once. The practical split is by source, because law, regulation, standard, and contract each change through a different process you have to watch.
How do compliance requirements differ from a compliance program?
The requirements are the obligations; the program is the system that meets them. The DOJ Evaluation of Corporate Compliance Programs tests the program on three questions: is it well designed, is it resourced and empowered, and does it work in practice. A complete list of compliance requirements with no owners, testing, or reporting fails the second and third questions.
What happens if compliance requirements are not met?
The consequence depends on the source: statutory breaches bring fines and, for individuals, prosecution, as Scoular’s FCPA resolution in July 2026 ($9,769,521 plus forfeiture) shows. Regulatory breaches bring orders and corrective action plans, as OSF Healthcare’s $552,250 HIPAA settlement did. Standard breaches cost certification, contract breaches cost the contract, and reputational damage follows all four.
How do small businesses manage compliance requirements?
The same register, with fewer lines. A small business identifies the ten to thirty compliance requirements with real penalties, assigns each to a named person, sets the evidence and the date, and reviews the list quarterly. OSHA’s 2026 penalty policy gives firms with 25 or fewer employees up to 70% size reductions, earned only by documented good faith.
Which international compliance requirements apply to US companies?
The FCPA applies to bribery abroad by US issuers and domestic concerns. GDPR applies to any company processing EU residents’ data, with fines up to 4% of global turnover under Article 83. The EU AI Act’s transparency duties applied from August 2, 2026, high-risk obligations follow on December 2, 2027, and sanctions rules cover every cross-border shipment and payment.
How often should compliance requirements be reviewed?
The register is reviewed in full annually and on every trigger: a new law or rule affecting a listed CFR part, a revised standard, a new contract with compliance clauses, or a merger. Horizon scanning runs weekly with a 30-day limit for impact notes. Individual lines are tested at the frequency the monitoring plan sets, from continuous to annual.
What Goes Wrong and the Fixes That Work
| Failure in managing compliance requirements | How it shows up | Fix |
| Requirements paraphrased from memory | Register says ‘annual HIPAA review’ with no clause cited; the owner cannot tell what the rule requires | Quote or cite the clause on every line; link to the primary text |
| Ownership by department | ‘IT’ owns encryption; nobody answers when the auditor calls | Role with named deputy; ownership confirmed at each review |
| Separate scoring scale | Compliance risks cannot be compared with cyber or operational risk at the board | Use the enterprise likelihood and impact scale in the register |
| Third parties outside the register | Customs brokers, resellers, and processors act for you without diligence | A register line per high-risk third-party class, with renewal dates |
| Self-disclosure decision left to the moment | Credit lost because the report reached the regulator late, as in the Scoular DPA | Pre-agreed escalation and disclosure protocol signed by the board |
| Monitoring equals training completion | 100% completion reported while control tests are not run | Six indicators, tested controls, hotline metrics, and overdue lines |
| Change scanned annually | Register carries a deadline that moved, such as the AI Act’s Annex III date | Weekly scanning with a 30-day impact note and dated register updates |
| Tool bought before the register exists | Software configured to a vendor’s generic library rather than your obligations | Register first, process second, platform third |
Where the Requirements Are Heading After 2026
Expect fewer federal compliance requirements and more individual accountability. The 2025 Federal Register ran at its lowest pace since the early 1990s, while the SEC named individuals in two-thirds of standalone actions and the DOJ set a False Claims Act record with 1,297 whistleblower suits. Fewer requirements, enforced harder against named people, is the pattern for the next two years.
State privacy law generates compliance requirements faster than federal law. California’s three 2026 penalties totalled $16.6 million by May, and the GM settlement added a five-year ban on data sales to consumer reporting agencies. Thomson Reuters lists data privacy and AI ethics among its ten global compliance concerns for 2026; both arrive through state and foreign rules first.
AI governance joins the list of compliance requirements. The DOJ already asks whether business AI is under compliance oversight, and the EU’s high-risk obligations now land on December 2, 2027 for Annex III systems and August 2, 2028 for Annex I products, per Gibson Dunn’s summary of the omnibus. Put both dates in the register now and assign the impact assessment.
Culture will decide which programs pass the DOJ’s third test. A register with objective triggers only works if the person who sees a trigger reports it, and the FY2025 qui tam record shows what happens when they report it elsewhere. Our guide to risk culture and the insider threat risk assessment template cover the two sides of that problem.
If you have a list of compliance requirements but no register with owners, evidence, ratings, and triggers, we build one from your contracts, permits, and regulatory footprint, score it on your enterprise scale, and hand it over with the monitoring plan and board report format. Read about our services, then contact us to start with the top twenty lines.
Chris Ekai is a Risk Management expert with over 10 years of experience in the field. He has a Master’s(MSc) degree in Risk Management from University of Portsmouth and is a CPA and Finance professional. He currently works as a Content Manager at Risk Publishing, writing about Enterprise Risk Management, Business Continuity Management and Project Management.
I blog often and I really appreciate your content.
This great article has really peaked my interest. I will
book mark your site and keep checking for new information about once per week.
I opted in for your RSS feed too.