An OT risk assessment is the structured evaluation of the threats, vulnerabilities, and consequences that could affect operational technology: the PLCs, HMIs, SCADA servers, and networks that run physical processes. It scopes the system, partitions it into zones and conduits, rates each risk against safety and production consequences, and sets a target security level for every zone.
Over the night of July 26 and 27, 2026, Iranian-affiliated actors changed passwords and IP addresses on programmable logic controllers at more than 30 community water systems in Minnesota. In Braham, population about 1,700, the well and treatment plant shut down until operators restored it by hand roughly two hours later.
CISA’s advisory AA26-097A, first published April 7, 2026 and updated July 22, had already described the technique: Rockwell, Schneider, and Siemens PLCs reachable from the internet on ports 44818, 2222, 102, and 502, project files exfiltrated, and shutdown and alarm logic disabled. By August 27, utilities in 12 states had reported incidents.
| OT Risk Assessment: Key Takeaways |
| An OT risk assessment rates the likelihood and consequence of cyber and physical events against the equipment that runs a plant, a grid, or a water system. Consequence is measured in safety, environmental, and production terms first, and in data terms second. |
| On July 26 and 27, 2026, Iranian-affiliated actors reached PLCs at more than 30 Minnesota community water systems through internet-exposed cellular modems. CISA counted more than 100 exposed water-sector systems targeted that month, and 12 states reported incidents by August 27. |
| Two standards frame the work: NIST SP 800-82 Rev. 3 for the OT security program and IEC 62443-3-2 for the seven-step zone-and-conduit risk assessment that ends in a target security level for each zone. |
| Dragos tracked 119 ransomware groups hitting 3,300 industrial organizations in 2025, up from 80 groups in 2024. Sites with full OT visibility contained incidents in 5 days against an industry average of 42. |
| SANS found 21.5 percent of 330 ICS/OT organizations had an incident in the past year, half of them starting with unauthorized external access, and only 14 percent feel fully prepared. |
| The worked register below scores six risks for a mid-sized water utility. Two of them, an exposed PLC and a default HMI password, are exactly what the July 2026 attackers used. |
Nothing in the campaign was novel. The PLCs were on cellular modems with default or weak credentials, which is the first line of any OT risk assessment. The assessment exists to find that exposure before an adversary does, and to put a number on what happens when a lift station or a treatment plant loses control.
What an OT Risk Assessment Covers and How It Differs From IT
The OT risk assessment definition comes from two documents: NIST SP 800-82 Rev. 3, published September 2023, describes OT as the hardware and software that detect or cause changes in physical processes, and applies the SP 800-30 risk assessment method to it.
IEC 62443-3-2:2020 defines the security risk assessment for system design, with zones, conduits, and security levels.
The difference from an IT assessment is the consequence scale. An IT breach costs data; an OT event can injure people, release chemicals, or stop production. Dragos’s guide to the 62443 concepts puts it as a shift from confidentiality-first to availability-and-safety-first, and that ordering changes which controls score highest.
| Dimension | IT risk assessment | OT risk assessment |
| Consequence measured in | Data confidentiality, integrity, availability; regulatory fines | Injury, environmental release, lost production, equipment damage, then data |
| Asset lifespan | 3 to 5 years, patched monthly | 15 to 30 years; patching needs a maintenance window and vendor approval |
| Scanning | Active scans are routine | Active scans can crash a PLC; passive discovery or vendor tools first |
| Access model | Identity-centric, MFA at the edge | Network-centric; zones and conduits; physical mode switches on controllers |
| Primary standards | NIST CSF 2.0, ISO 27001, SP 800-30 | NIST SP 800-82 Rev. 3, IEC 62443-3-2, NERC CIP, CISA CPGs |
| Review trigger | Annual, or after a major change | Any process change, new remote access path, vendor visit, or an advisory naming your PLC model |
The scope is wider than the control network. The IEC 62443 risk assessment guide on this site covers the standard in detail, and the physical security guide covers cabinet locks and site access. An OT risk assessment that omits the cellular modem or the unlocked cabinet has left out the two most common entry paths.
| Term | Meaning in OT risk assessment | July 2026 example |
| System under consideration | The plant, process, or facility boundary being assessed | Braham’s well, treatment plant, and their PLCs |
| Zone | A grouping of assets with the same security requirements | Treatment control zone; lift station zone; remote telemetry zone |
| Conduit | A communication path between zones | Cellular modem link from a lift station PLC to the SCADA server |
| Security level target (SL-T) | The protection a zone needs, from SL 1 to SL 4 | SL 2 or higher for any zone reachable from outside the plant |
| Consequence | The physical or operational result of a successful attack | Loss of view and control; pressure loss; manual operation for two hours |
Why the Assessment Is Overdue at Most Plants
The case for an OT risk assessment now rests on what adversaries did in 2025 and 2026. Dragos’s 2026 Year in Review, released February 17, 2026, tracked 119 ransomware groups affecting 3,300 industrial organizations in 2025, a 49 percent rise in groups from 80 the year before. Manufacturing supplied two-thirds of the victims.
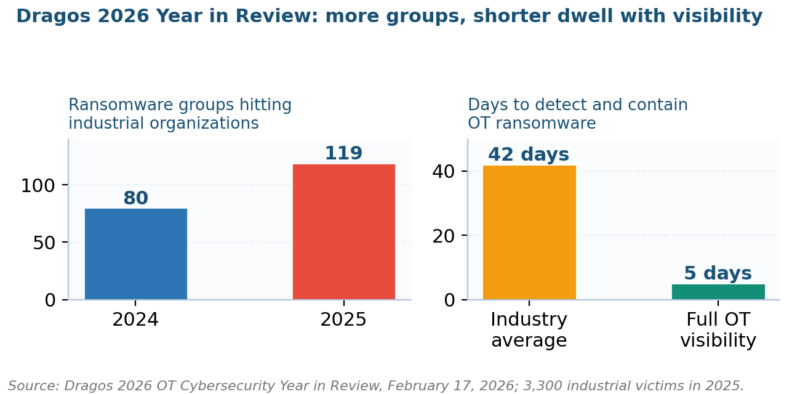
Figure 1. Ransomware group count and containment time from the Dragos 2026 OT Cybersecurity Year in Review.
Dragos CEO Robert M. Lee described adversaries mapping how control systems work, where commands originate, and where physical effects can be induced. The report named three new groups, AZURITE, PYROXENE, and SYLVANITE, and found that sites with full OT visibility contained ransomware in an average of 5 days against 42 for the industry.
Europe supplied the destructive case. In December 2025, actors wiped HMIs and corrupted RTU firmware at Polish renewable plants and a combined heat and power plant, cutting view and control between facilities and distribution operators. CISA’s February 10, 2026 alert drew on CERT Polska’s report and told US operators to change default passwords and plan for inoperative devices.
The survey data behind any OT risk assessment points the same way. SANS’s State of ICS/OT Security 2025 found 21.5 percent of 330 respondents had an incident in the past year, and half began with unauthorized external access. Fortinet’s 2025 report found 60 percent of intrusions spanned both IT and OT, up from 49 percent.
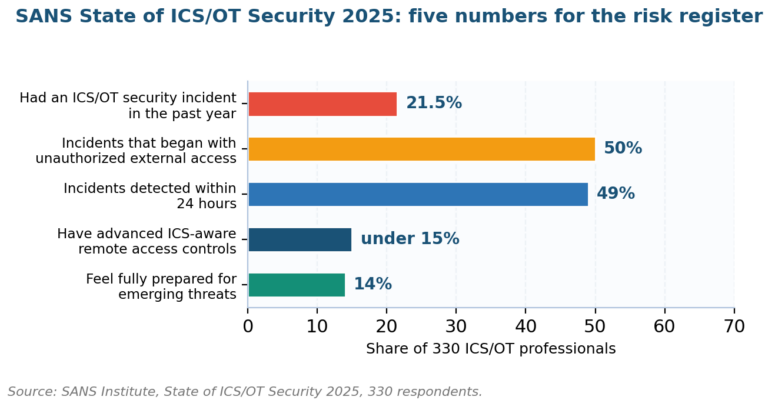
Figure 2. Five findings from the SANS Institute survey of 330 ICS/OT professionals, 2025.
Two SANS numbers matter for the register. Fewer than 15 percent of organizations have advanced ICS-aware remote access controls, and only 14 percent feel fully prepared for emerging threats. Industrial Cyber’s summary of the Fortinet data adds that 65 percent of the most mature organizations reported zero intrusions, against 46 percent at the lowest maturity levels.
The Seven Steps of an OT Risk Assessment Under IEC 62443-3-2
IEC 62443-3-2 lays out the assessment as seven zone and conduit requirements, ZCR 1 through ZCR 7. The sequence starts with the system boundary and ends with an approved cybersecurity requirements specification. The ISA’s overview of the series explains where part 3-2 sits among the other thirteen documents, and our second 62443 guide works through the security-level maths.
| Step | What you do | Output | Common shortcut that fails |
| ZCR 1: Identify the system under consideration | Draw the boundary; build the asset inventory from passive discovery, vendor lists, and a site walk | Asset list with make, model, firmware, network address, physical location | Inventory built from the IT CMDB, which omits the cellular modems |
| ZCR 2: Initial risk assessment | Rate worst-case consequence per asset without considering controls | Ranked list of high-consequence assets | Rating likelihood before consequence; a rare event that kills someone still scores high |
| ZCR 3: Partition into zones and conduits | Group assets with the same security needs; list every path between groups | Zone and conduit diagram | One flat zone for the whole plant |
| ZCR 4: Determine tolerable risk | Agree with the board what consequence and likelihood the organization accepts | Risk appetite by consequence category | Skipped, so every finding is argued case by case |
| ZCR 5: Detailed risk assessment | For zones above tolerable risk, list threats, vulnerabilities, existing controls, and residual risk | Detailed register per zone | Assessing only the zones IT can see |
| ZCR 6: Document requirements | Set the SL-T for each zone and conduit and specify the controls that reach it | Cybersecurity requirements specification | SL-T set without checking the PLC can support it |
| ZCR 7: Approval | Asset owner signs the specification; funding and dates attached | Signed specification, project plan | Approval without a budget line, so nothing changes |
Step one decides the quality of the whole OT risk assessment. The July 2026 attackers reached devices that were on the network but not on the inventory, which is why risk identification in OT starts with a physical walk and a passive network capture. The risk assessment pillar describes the generic sequence this maps to.
Steps two and five use the same likelihood and consequence scales as the rest of the complete risk assessment guide, with consequence categories for safety, environment, production, and equipment. We rate consequence first and likelihood second in OT, because a control failure that could injure someone does not become acceptable by being rare.
An OT risk assessment is only as good as the documents on the table when ZCR 1 starts, and the July 2026 utilities had almost none of them. We ask for the six items below before the first site walk, because each one closes a gap the attackers used:
- Network diagrams as built, not as designed, including every cellular, dial-up, and vendor remote access path
- The vendor’s list of installed controllers and firmware versions, checked against CISA’s Known Exploited Vulnerabilities catalog
- Alarm and shutdown logic exports from each PLC, so unauthorized changes can be detected later
- Maintenance records showing when each device was last patched or replaced
- Incident and near-miss logs for the past three years, including loss-of-view events blamed on hardware
- The site’s safety instrumented system documentation and its independence from the control network
Step four is where most programs stall. Tolerable risk has to be set by the asset owner in consequence terms, and the risk appetite guide shows how to phrase it. For a water utility: no tolerance for loss of control of chlorination; low tolerance for loss of view lasting more than 30 minutes at any lift station.
A Worked Register for a Mid-Sized Water Utility
The OT risk assessment register below applies steps two and five to a utility serving about 80,000 people with two water towers, a treatment plant, and eight wastewater lift stations on cellular telemetry, the profile of Plymouth, Minnesota. Scales run 1 to 5 for likelihood and consequence. Build your own with the register template.
| Zone and risk | Threat scenario | Inherent (L x C) | Controls to reach SL-T | Residual |
| Lift station telemetry zone: PLC reachable via cellular modem | Actor scans port 44818, logs in with default credentials, changes IP and password, operators lose view | 5 x 4 = 20 | Modem behind a secure gateway with MFA; PLC mode switch set to run; unique credentials; port monitoring | 2 x 4 = 8 |
| Treatment control zone: HMI with default password | Actor alters displayed chlorine residual so operators act on false data | 4 x 5 = 20 | Unique credentials; HMI on an isolated zone; independent analyzer alarm not routed through the HMI | 1 x 5 = 5 |
| Treatment control zone: PLC project file exfiltrated | Actor downloads logic, disables shutdown and alarm rungs, re-uploads | 3 x 5 = 15 | Project file integrity checks; offline signed backups; change alerts from the engineering workstation | 1 x 5 = 5 |
| IT to OT conduit: flat network from billing to SCADA | Ransomware on a billing laptop reaches the SCADA server | 4 x 4 = 16 | Firewall with allow-list rules; jump host for engineering access; no shared credentials | 2 x 4 = 8 |
| Water tower zone: level sensor spoofed | False low-level reading drives pumps to overflow the tower | 2 x 4 = 8 | Plausibility check against flow meters; high-level float switch hardwired to pump cut-out | 1 x 4 = 4 |
| Vendor remote access conduit: integrator VPN always on | Compromised integrator credentials used to reach every site | 3 x 5 = 15 | Time-boxed access enabled per ticket; session recording; vendor assessed with the questionnaire | 1 x 5 = 5 |
The first two rows are the July 2026 attack, and their controls cost less than the emergency call-out. A secure gateway for a cellular modem is a few hundred dollars per site; the mode switch is already on the controller. The bow-tie method is a useful way to present each row to a board that has never seen a PLC.
Row six is the one most utilities forget. CISA’s advisory documents project-file exfiltration through the vendor’s own configuration software, and the vendor questionnaire plus the supply chain guide cover how to assess the integrator who holds standing access to every site. The residual column is the number that goes to the board.
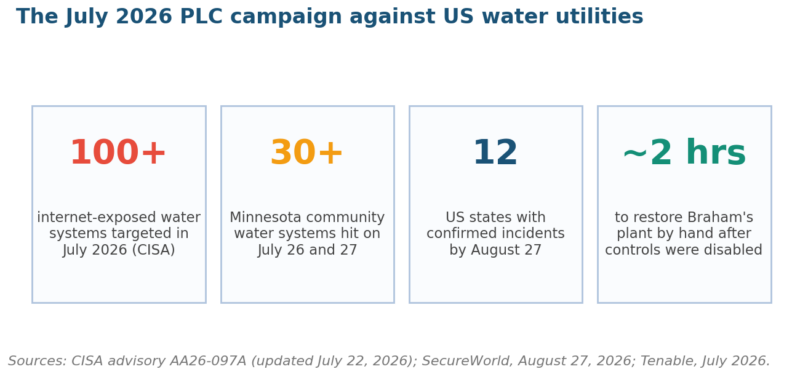
Figure 3. The July 2026 campaign against US water utilities in four figures, from CISA, SecureWorld, and Tenable.
The OT risk assessment register also sets the monitoring plan. Each residual rating needs an indicator that would show it drifting, and the energy and utilities KRI set lists the ones that fit a utility: exposed devices per scan, days since the last firmware review, vendor sessions outside a ticket. The cybersecurity KRI template gives the thresholds.
Matching Controls to Target Security Levels and Regulations
A target security level from an OT risk assessment is only useful if it maps to controls someone can configure. IEC 62443-3-3 lists the system requirements per level, and CISA’s Cross-Sector Cybersecurity Performance Goals give a plain-language baseline near SL 1 and SL 2 for utilities without a security team. The risk controls guide explains the control types.
| Level | Protects against | Typical controls | Where it fits |
| SL 1 | Casual or coincidental violation | Unique passwords, network segmentation, backups, basic logging | Non-critical monitoring zones |
| SL 2 | Intentional attack with simple means and low resources | MFA on remote access, allow-list firewalls, integrity checks on project files, mode switches | Any zone reachable from outside the plant; the July 2026 attackers operated at this level |
| SL 3 | Sophisticated means, moderate resources, ICS-specific skills | Application allow-listing, OT-aware intrusion detection, signed firmware, hardened engineering workstations | Treatment and safety-adjacent zones; NERC CIP medium-impact assets |
| SL 4 | Extended resources, nation-state capability | Physical separation, dual-approval changes, continuous monitoring with response staff | Safety instrumented systems; NERC CIP high-impact control centers |
Regulation sets the floor by sector. NERC CIP is mandatory for bulk electric system assets, the EPA’s water cybersecurity program supports the AWIA risk and resilience assessments that Foley Hoag notes apply to systems serving more than 3,300 people, and CIRCIA incident-reporting rules are expected in final form in September 2026.
For threat modelling inside steps two and five, the MITRE ATT&CK for ICS matrix lists the techniques the July attackers used: exploitation of remote services, modify program, and loss of view. Pair it with CISA’s ICS advisories and the KEV catalog to keep the vulnerability column current, and use the cyber risk management framework for the program around it.
Dragos found that 25 percent of ICS-CERT and NVD vulnerabilities in 2025 carried incorrect CVSS scores and 26 percent of advisories shipped with no vendor patch or mitigation. Only 2 percent qualified as patch-now. That is why the register rates consequence for your process rather than copying a severity score, and why scenario-based assessment outperforms a vulnerability list.
Where OT Risk Assessment Programs Go Wrong
Every consent order and advisory cited above describes the same handful of failures, and none of them is technical. The table collects the ones that recur in the 2025 and 2026 incidents, with the correction that costs least. The types of risk assessment guide explains why OT needs its own method rather than a copy of the IT one.
| Failure | Where it appeared | Correction |
| Inventory taken from the IT asset database | Minnesota utilities did not know which PLCs sat on cellular modems | Passive network capture plus a site walk; every modem, dial-up line, and vendor VPN listed as a conduit |
| Default credentials left in place | AA26-097A, the Polish plants, and the 2023 Aliquippa attack all used them | Unique credentials as a ZCR 1 finding closed before the assessment report is issued |
| Likelihood rated before consequence | Rare high-consequence events scored as low risk | Consequence first; any injury or environmental release scenario goes to detailed assessment regardless of likelihood |
| One zone for the whole plant | Ransomware moved from billing systems to SCADA | Zones by consequence; conduits with allow-list rules; jump host for engineering |
| Tolerable risk never set | Every finding argued case by case; nothing funded | Board-approved appetite by consequence category before ZCR 5 |
| SL-T set above what the equipment supports | Requirements specification unreachable on a 2008 controller | Check the vendor’s 62443-4-2 capability level first; use compensating controls in the zone |
| No re-assessment trigger | Assessment dated 2022 while the modem was installed in 2024 | Triggers: any new remote path, process change, vendor visit, or an advisory naming an installed model |
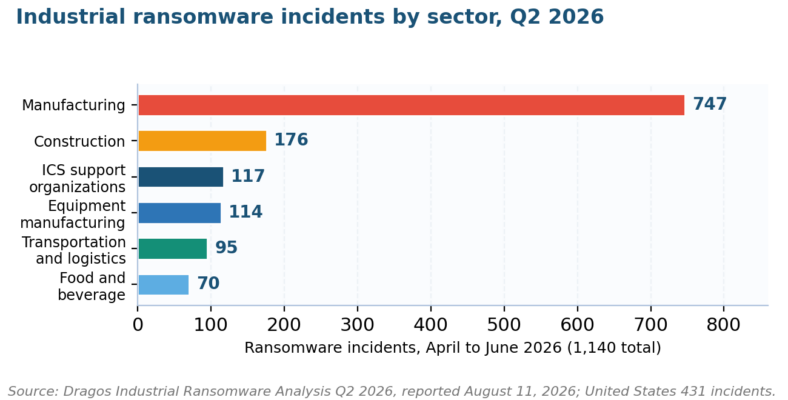
Figure 4. Industrial ransomware incidents by sector, April to June 2026, from the Dragos quarterly analysis.
Figure 4 gives the OT risk assessment likelihood column a source. Dragos counted 1,140 industrial ransomware incidents in the second quarter of 2026, up 12 percent from 1,020 in the first, with 431 in the United States and manufacturing supplying 747. Mackay Sugar’s two Queensland mills stopped on June 10 with no evidence the attackers reached the ICS at all.
That last detail is the argument for row four in the table. Most industrial ransomware never touches a controller; it stops production by taking down the IT systems the plant depends on. The disaster recovery plan template and the business continuity program guide cover the manual-operation side that kept Plymouth’s water running.
Frequently Asked Questions About OT Risk Assessment
What is an OT risk assessment in simple terms?
An OT risk assessment lists the equipment that runs a physical process, works out how an attacker or a fault could make it misbehave, rates how bad that would be for people, the environment, and production, and decides which protections each part of the system needs. The output is a zoned diagram, a scored register, and a requirements specification.
How is an OT risk assessment different from an IT risk assessment?
The consequence scale comes first. An OT risk assessment measures injury, environmental release, and lost production before data loss, tolerates no active scanning that could crash a controller, and works with equipment that stays in service for decades. The IT risk management lifecycle covers the office side of the same organization.
What standards apply to an OT risk assessment?
NIST SP 800-82 Rev. 3 for the program and IEC 62443-3-2 for the seven-step zone-and-conduit method are the two references for any OT risk assessment. NERC CIP covers bulk electric assets, AWIA assessments cover water systems serving more than 3,300 people, and CISA’s performance goals give a baseline for any sector, while ISO 31000 supplies the generic vocabulary.
How often should an OT risk assessment be repeated?
Annually at minimum, and on any trigger: a new remote access path, a process or equipment change, a vendor visit that touched a controller, or a CISA advisory naming a model you run. The July 2026 update to AA26-097A was a trigger for every utility with Rockwell, Schneider, or Siemens PLCs, four days before the Minnesota attacks.
Who should carry out an OT risk assessment?
A joint team: the process engineer who knows what each controller does, the automation or instrument technician who knows how it is wired, and a security specialist familiar with IEC 62443. The asset owner signs the tolerable-risk statement and the final specification. Outsourcing the whole exercise to an IT firm produces an inventory without the modems.
What does an OT risk assessment deliver?
Six documents: an asset inventory with firmware and location, a zone-and-conduit diagram, a scored risk register with residual ratings, a tolerable-risk statement, a cybersecurity requirements specification with a target security level per zone, and a monitoring plan with indicators. The risk assessment tool guide lists the techniques used to fill each one.
How do you score risk in an OT risk assessment?
Rate consequence on a 1 to 5 scale across safety, environment, production, and equipment, take the highest, then rate likelihood on the same scale using threat intelligence and exposure. Multiply for an inherent score, apply the existing controls, and record the residual. The risk matrix template and the risk analysis guide walk through the arithmetic.
What Changes for OT Operators Before 2027
Two deadlines shape the next OT risk assessment cycle. CIRCIA reporting rules, expected in final form in September 2026, will require covered critical infrastructure entities to report substantial cyber incidents within 72 hours, which means the register has to name who decides what counts as substantial. The risk response guide covers the decision path.
The second is the NIST Cybersecurity Framework 2.0 Govern function, now written into most utility grant conditions, which asks for a documented risk appetite and named accountability. That is ZCR 4 and ZCR 7 in the language a grant reviewer uses. Dragos’s first-quarter analysis already shows attackers shifting from reconnaissance to disruption.
Start with the modems: list every cellular, dial-up, and vendor path into a controller, change every default credential, and set each PLC mode switch to run. Those three actions close the top two register rows and would have kept the July 2026 actors out. The cyber security risk management plan turns the rest of the register into a funded schedule.
When a plant needs its first zone-and-conduit OT risk assessment, or an old one re-scored against the 2026 advisories, we run the seven steps with the process engineers. The services page describes the format; the contact page is where to start. Braham restored its plant in two hours; the OT risk assessment that prevents the outage takes two days.
Chris Ekai is a Risk Management expert with over 10 years of experience in the field. He has a Master’s(MSc) degree in Risk Management from University of Portsmouth and is a CPA and Finance professional. He currently works as a Content Manager at Risk Publishing, writing about Enterprise Risk Management, Business Continuity Management and Project Management.