Risk controls are the specific policies, procedures, system settings, and checks an organization puts in place to reduce the likelihood or the impact of a risk. Each control has an owner, a frequency, and evidence that it ran. Examples include approval limits, bank reconciliations, multifactor authentication, and backup restores.
On January 27, 2026, the Securities and Exchange Commission charged Archer-Daniels-Midland and three former executives. ADM agreed to a $40 million civil penalty. According to the SEC’s announcement, intersegment adjustments, including retroactive rebates not offered to outside customers, moved operating profit into the Nutrition segment.
The aim, the SEC said, was to make Nutrition appear to meet the 15% to 20% annual profit growth executives had projected. The order found internal accounting controls violations, and ADM’s remediation added risk controls over intersegment transactions plus testing of them. Controls must cover the transactions that matter.
| The Bottom Line |
| Risk controls are the specific measures an organization uses to reduce the likelihood or impact of a risk: approvals, reconciliations, access limits, monitoring, backups, and similar actions with a named owner and evidence that they ran. |
| Classify risk controls by purpose (preventive, detective, corrective, directive, compensating) and by how they run (manual, automated, IT-dependent manual). Most sound processes mix preventive and detective controls. |
| In January 2026 the SEC fined ADM $40 million after intersegment adjustments shifted profit into its Nutrition segment; the order cited internal accounting controls violations, and ADM’s remediation included new controls over those transactions. |
| The ACFE’s 2026 study of 2,402 fraud cases found a lack of internal controls was the main weakness in 33% of cases, override of controls in 19%, and lack of management review in 18%. |
| A control is effective only when it is well designed and operates as designed. Rate both, test with evidence, and let the result set the residual risk score. |
| Every control needs an owner in the first line, oversight from the second line, and periodic independent testing from internal audit. |
What Risk Controls Are, and What They Are Not
Standards define a control in almost the same words. NIST’s glossary, drawing on SP 800-53, defines a control as a measure that is modifying risk. ISO 31000:2018 uses nearly identical wording, and its risk treatment options range from avoiding the risk to retaining it by informed decision, and risk controls carry out most of those treatment decisions.
COSO’s Internal Control Integrated Framework, updated in 2013, puts controls inside its control activities component. The COSO executive summary names authorizations, verifications, reconciliations, reviews, and segregation of duties as examples, and notes that control activities may be preventive or detective and manual or automated.
| Term | What it means | How it relates to risk controls |
| Risk | The effect of uncertainty on objectives, scored by likelihood and impact | The thing a control acts on |
| Risk treatment | The decision to avoid, reduce, share, or retain a risk | Controls deliver the reduce option and support the others |
| Control | A specific measure with an owner, frequency, and evidence | The unit you design, test, and rate |
| Policy | A statement of intent or a rule | Not a control by itself; the check that enforces it is the control |
| Key risk indicator | A metric that warns when exposure rises | Monitors whether risk is moving despite controls |
| Residual risk | The risk left after controls operate | The result of inherent risk minus control effect |
The most common mistake is listing a policy as a control. A travel expense policy states the rule; the manager’s review of each claim against receipts is the control. If nobody can show evidence that a check ran last month, it is not working as a control, whatever the policy manual says.
Risk controls also differ from risk management as a whole. Risk management covers identification, assessment, treatment, and monitoring across the organization; controls are the measures used in the treatment step.
Our comparison of risk assessment and risk management and the guide to risk response planning show where controls sit in that cycle.
The Five Types of Risk Controls by Purpose
Most frameworks sort risk controls by what they do relative to the risk event. Preventive controls act before the event, detective controls find it after it starts, and corrective controls limit the damage. Directive and compensating controls complete the set, and NIST defines compensating controls as measures used in place of a baseline control that give equivalent protection.
| Type | Purpose | Examples | Main limitation |
| Preventive | Stop an error or loss event from happening | Approval limits, segregation of duties, MFA, input validation, locked storage | Can slow the process and invites workarounds |
| Detective | Find an event soon after it occurs | Reconciliations, exception reports, log monitoring, surprise audits | Loss may occur before detection |
| Corrective | Limit damage and restore normal operation | Backup restores, wire recall procedures, incident response, patching | Depends on fast detection |
| Directive | Guide behavior toward the desired outcome | Policies, procedures, training, code of conduct | Weak unless backed by a check |
| Compensating | Cover for a control that cannot be applied | Supervisor review where a small team cannot split duties | Often more costly per transaction |
A useful way to see the difference is the bow-tie diagram. Preventive controls sit on the left, between the causes and the risk event, while detective and corrective controls sit on the right, between the event and its consequences. A process with controls on only one side is exposed on the other.
Safety programs use a different scale for the same idea. The hierarchy of controls ranks elimination first, then substitution, engineering controls, administrative controls, and personal protective equipment last.
Physical risk controls such as guards and interlocks are engineering controls in that scheme, and they are more reliable than a procedure that depends on people remembering it.
For information security, ISACA’s list of specific controls names antivirus and MFA as preventive and security monitoring as detective.
The NIST SP 800-53 Revision 5 catalog organizes hundreds of security and privacy controls into 20 families, from access control to supply chain risk management.
The table below applies the three main types across common risk categories. It is a starting list for a workshop, and our risk management techniques guide and the article on how to mitigate risk in business give more options per category.
| Risk category | Preventive control | Detective control | Corrective control |
| Payment fraud | Dual approval and call-back for vendor bank changes | Weekly vendor master change report | Wire recall procedure with the bank |
| Cyber intrusion | MFA and least-privilege access | Security log monitoring and alerts | Isolate host and restore from backup |
| Financial reporting | Journal entry approval by a second person | Account reconciliations and variance review | Correcting entries and root-cause fix |
| Regulatory compliance | Mandatory checklist before product launch | Compliance testing and complaint trend review | Remediation plan and regulator notice |
| Workplace safety | Machine guarding and lockout procedures | Inspections and near-miss reporting | First aid, incident investigation |
| Supply disruption | Dual sourcing for critical parts | Supplier performance and financial alerts | Activate backup supplier and safety stock |
Manual, Automated, and IT-Dependent Controls
Risk controls also differ by how they run: a manual control relies on a person, such as a controller. An automated control is performed by a system, such as a three-way match that blocks an invoice. An IT-dependent manual control is a person reviewing a system report, so its reliability depends on the report being complete and accurate.
| Nature | Example | Strength | What must also be tested |
| Manual | Manager signs off on expense claims | Handles judgment and unusual cases | Evidence of review on a sample of items |
| Automated | System blocks payment without a matched receipt | Consistent every time | IT general controls over change and access |
| IT-dependent manual | Controller reviews a user-access report | Combines system data with judgment | Completeness and accuracy of the report |
| IT general control | Change approval before code moves to production | Protects all automated controls | Change tickets, approvals, and access logs |
COSO Principle 11 exists because automated controls are only as good as the technology around them. If anyone can change the matching rule without approval, the automated control cannot be relied on.
That is why auditors test IT general controls over access and program change before they rely on an automated control.
Automation is growing, though unevenly. In Protiviti’s 2025 SOX compliance poll, 68% of respondents named more technology and automation as a top improvement area, 61% used audit management or GRC platforms, and 24% used AI or machine learning tools. We expect automated controls to take a larger share of key controls over the next three years.
Why Controls Fail: What the Fraud and Audit Data Show
The best evidence on control failure comes from fraud cases. The ACFE’s Occupational Fraud 2026 report studied 2,402 cases in 143 countries with a median loss of $104,000, and the ACFE estimates organizations lose 5% of revenue to fraud each year. Control weaknesses explain most of those losses.
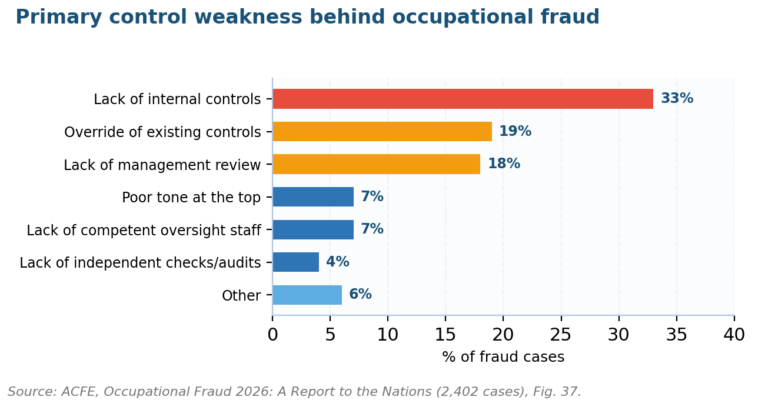
Missing controls, overridden controls, and missing management review together explain 70% of the fraud cases in the ACFE’s 2026 study.
Three weaknesses dominate: no control in place (33%), override of an existing control (19%), and no management review (18%). The second figure matters most for design. A control that a senior manager can bypass without leaving a record gives little protection, which is why segregation of duties and system-enforced approvals outperform instructions.
The same study shows which controls cut losses. Median losses were 55% lower where management review was in place, 53% lower with proactive data monitoring, and 50% lower with surprise audits. Tips detected 43% of frauds, so a working hotline is itself a detective control worth rating.
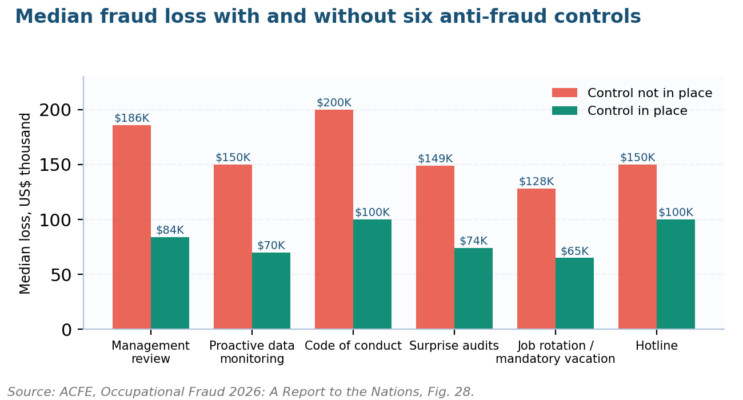
Each control is associated with a lower median loss; the ACFE reports association across cases, not a controlled experiment.
Regulators see the same pattern. NYDFS fined Block $40 million in April 2025 after Cash App’s rapid growth left a severe alert backlog, and Superintendent Adrienne Harris said compliance functions must keep pace with company growth. In February 2025 FinCEN fined Brink’s $37 million for moving currency without required AML controls.
Public company reporting has improved. Baker Tilly’s analysis found adverse internal control assessments fell from over 26% of filers in 2021 to just over 15% in 2024, with revenue recognition the most common problem area. The PCAOB’s 2024 inspection Spotlight reported the Big Four deficiency rate fell to 20% from 26%.
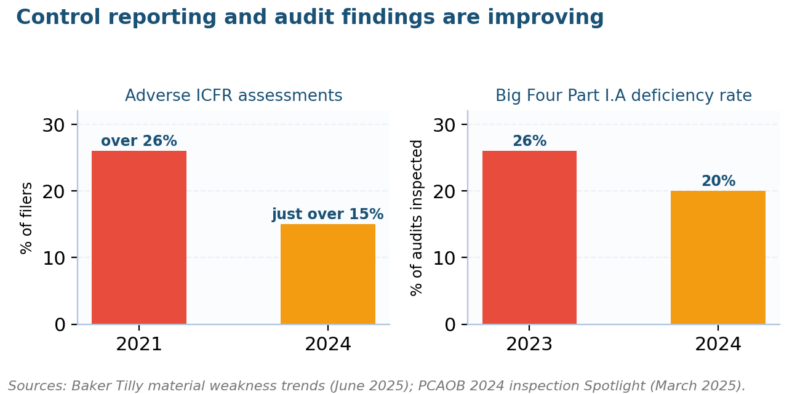
Fewer adverse control opinions and fewer audit deficiencies, but review controls remain the most common testing problem.
The PCAOB still found that auditors often failed to test review controls properly, and in smaller companies missed the risk that one person could prepare and post journal entries without approval. Enforcement continues too: SEC public company actions fell to 56 in fiscal 2025, with total settlements of $808 million, according to Cornerstone Research data.
How to Design Risk Controls That Work
Design starts with the risk, not the control library. COSO Principle 10 says an organization selects and develops control activities that reduce risks to acceptable levels, Principle 11 covers technology controls, and Principle 12 says controls are deployed through policies and procedures. The COSO internal control guidance treats all three as required for an effective system.
A well-designed control answers the same questions every time, and each missing answer is a design gap that testing will later expose. We check every one of our clients’ risk controls against these six attributes before it goes into the register:
- Who performs it: a named role, independent of the person whose work is checked
- What exactly is done: compare, approve, reconcile, block, or review, with the criteria stated
- When and how often: per transaction, daily, weekly, monthly, or quarterly
- What threshold triggers follow-up: for example, any variance above $5,000 or 2%
- What happens to exceptions: who investigates, by when, and how resolution is recorded
- What evidence is kept: sign-off, system log, ticket, or report, and where it is stored
Link each control to a specific cause of the risk. If the risk is payment to a fraudulent vendor, the causes include fake vendor creation, changed bank details, and duplicate invoices, and each needs its own control. Our guide to risk register structure shows how to record cause, control, and owner on one row.
Size controls to your risk appetite. A control that costs more than the loss it prevents is poor design, and too many low-value checks slow the business and lead people to approve without checking. The risk appetite statement examples help set the tolerance each control is meant to keep the risk within.
Mark key controls clearly. A key control is one that, if it failed, would leave a significant risk without adequate cover, so it gets tested first and more often. Banks describe the same expectation in the Basel Committee’s principles for sound operational risk management, and our guide to operational risk management in banking applies them.
Testing and Rating Control Effectiveness
Risk controls have two separate qualities: design effectiveness asks whether the control, operated as described, would address the risk. Operating effectiveness asks whether it actually ran as described over the period. Auditors assess design through walkthroughs and operation through testing a sample, and both must pass before the control is relied on.
| Test method | What the tester does | Evidence strength | Best used for |
| Inquiry | Asks the control owner how the control works | Weakest; never enough alone | Understanding the process |
| Observation | Watches the control being performed | Moderate; only proves that moment | Physical and real-time controls |
| Inspection | Examines documents, sign-offs, logs, or tickets | Strong when evidence is complete | Reviews and approvals |
| Reperformance | Performs the control again independently | Strongest | Reconciliations and calculations |
Sample sizes rise with frequency. As a starting point, many teams test one instance of an annual control, two of a quarterly control, two to five of a monthly control, and 25 or more of a daily or per-transaction control. Your external auditor’s methodology governs where results support financial statement reliance.
Rate the result on a simple scale. We use three levels: effective, partially effective, and ineffective, and a control is rated no higher than its weaker dimension. A strong design with test exceptions is partially effective; a weak design is ineffective however faithfully it runs.
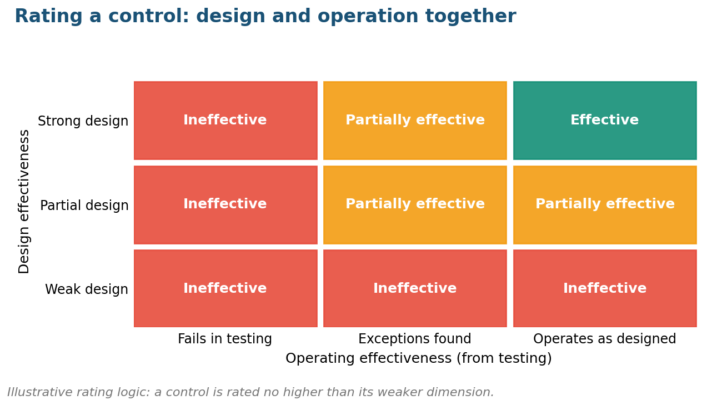
Design and operation are rated separately, then combined. Only a strong design that operates as designed earns an effective rating.
The rating feeds the residual score. An effective control might reduce likelihood or impact by two points on a five-point scale, a partial one by one point, and an ineffective one by none. Our guide to inherent and residual risk explains the arithmetic, and the 5×5 risk matrix comparison covers the scales.
Between tests, key control indicators show whether controls are still running. Examples include the number of reconciliations completed late, open exceptions past due, and access reviews not signed off. Our guide to developing key risk indicators and the list of operational risk KRI examples include several that work as control indicators.
Worked Example: A Control Register for Vendor Payments
Here is a control set for one risk: payment to a fraudulent or altered vendor account at a mid-sized distributor. The inherent risk scores 4 for likelihood and 5 for impact, or 20 on a 25-point scale. Each row shows type, nature, frequency, whether it is key, and the test result.
| Control | Type | Nature | Frequency | Key | Test result |
| C1 Call-back and second approval for vendor bank changes | Preventive | Manual | Per change | Yes | Effective: 25 of 25 changes had call-back evidence |
| C2 Three-way match blocks unmatched invoices | Preventive | Automated | Per invoice | Yes | Effective: rule tested; change access limited |
| C3 AP staff cannot create or edit vendors | Preventive | IT-dependent | Continuous | Yes | Partially effective: two users with both roles |
| C4 Controller reviews weekly vendor change report | Detective | IT-dependent manual | Weekly | No | Partially effective: 3 of 10 weeks late |
| C5 Monthly bank reconciliation with review | Detective | Manual | Monthly | Yes | Effective: 3 of 3 months reviewed on time |
| C6 Positive pay file sent to the bank | Preventive | Automated | Daily | No | Effective |
| C7 Wire recall procedure within 24 hours | Corrective | Manual | On event | No | Design only: not yet exercised |
Two findings change the residual score. The role conflict in C3 means one person could set up a vendor and approve payment, which is the exact segregation gap the PCAOB highlights for journal entries. Late reviews in C4 weaken the detective layer that should catch what C3 misses.
With C1, C2, C5, and C6 effective, residual likelihood drops from 4 to 2 and impact from 5 to 4, giving 8. Fixing C3 by removing the two conflicting role assignments would take likelihood to 1. We would also run a tabletop exercise to test C7 before relying on it.
Record the result in your risk register template and review it through a risk and control self-assessment. Banks can use the RCSA template for banks, which applies the same design and operating ratings across business lines and feeds the operational risk profile.
Who Owns Each Control: The Three Lines
Ownership decides whether controls keep running. The IIA’s Three Lines Model, updated in 2020, puts management in the first line to own and operate controls, specialist risk and compliance functions in the second line to set standards and challenge, and internal audit in the third line to give independent assurance to the board.
| Role | Responsibility for controls | Typical activity | Output |
| First line: process owners | Design, operate, and self-assess controls | Perform reviews, fix exceptions, run RCSA | Signed control evidence, self-assessments |
| Second line: risk and compliance | Set standards and challenge ratings | Review control library, monitor KCIs | Risk profile and control reports |
| Third line: internal audit | Independently test controls | Walkthroughs and sample testing | Audit reports and ratings |
| Board or audit committee | Oversee the control system | Review key findings and remediation | Decisions and follow-up |
The model only works if the first line owns its controls. When the risk team writes control descriptions for managers, the controls become paperwork. Our explanation of the three lines of defense model covers common overlaps, and the internal audit work program templates show how the third line plans testing.
Self-assessment connects the first and third lines. A first-line control self-assessment gives internal audit a starting view, and staff who run these workshops can build skills through the CCSA certification. Internal audit teams can track their own coverage with internal audit KRIs.
Frequently Asked Questions About Risk Controls
What are the four main types of risk controls?
The four main types of risk controls are preventive, detective, corrective, and directive. Preventive controls stop an event, detective controls find it, corrective controls limit damage and restore operations, and directive controls guide behavior through policy and training. Many frameworks add compensating controls as a fifth type for cases where a standard control cannot be applied.
What are examples of risk controls?
Common examples of risk controls include approval limits, segregation of duties, bank reconciliations, multifactor authentication, exception reports, surprise audits, backup restores, and incident response procedures. Each becomes a real control only when it has a named owner, a set frequency, a threshold for follow-up, and evidence that it ran.
What is the difference between risk controls and risk management?
Risk management is the full process of identifying, assessing, treating, and monitoring risk across an organization. Risk controls are the specific measures used in the treatment step to reduce likelihood or impact. Risk management decides which risks need attention; controls do the work of keeping those risks within appetite.
How do you test whether risk controls are effective?
Test risk controls for design and for operation. Walk through the process to confirm the control would address the risk, then inspect or reperform a sample of instances to confirm it ran as described over the period. Rate the control no higher than its weaker result.
What is a key control in risk management?
A key control is one of the risk controls that, if it failed, would leave a significant risk without adequate cover. Key controls are tested first and more often, and their failure is reported to management. Non-key controls still matter but add less protection on their own.
Who is responsible for risk controls?
Process owners in the first line are responsible for designing and operating risk controls. Risk and compliance functions in the second line set standards and challenge control ratings, and internal audit in the third line tests controls independently. The board oversees the whole system through the audit or risk committee.
How often should risk controls be reviewed?
Review key risk controls at least once a year and whenever the process, system, or risk changes. Monitor control indicators such as late reconciliations monthly between tests. High-risk automated controls also need their IT general controls tested each year, because a system change can disable them without anyone noticing.
Lessons from Control Programs That Failed
Control programs fail in repeatable ways, and most of the fixes cost little. The ACFE, PCAOB, and enforcement cases above all point to the same handful of problems. The table sets out seven, each with the fix we recommend when we review a control library.
| Failure | What it looks like | Fix |
| Policy listed as a control | Register says ‘expense policy’ with no check named | Name the check, the reviewer, and the evidence |
| Controls cover routine items only | Unusual transactions, such as intersegment adjustments, have no review | Add controls for manual and non-standard entries |
| Management can override | A senior manager can approve their own exception | Require independent approval and log overrides |
| Review with no criteria | Sign-off with no stated threshold or follow-up | Define what the reviewer checks and what triggers action |
| Automated control without ITGCs | Matching rules can be changed without approval | Test change management and access first |
| Controls fall behind growth | Alert backlogs build as volume rises | Track control capacity with indicators |
| Ratings never tested | Self-assessed ‘effective’ ratings accepted as fact | Sample-test key controls independently each year |
The ADM case shows the second failure well. The SEC order says the problem sat in intersegment adjustments, and ADM’s fix was new controls over exactly those transactions. Volkov Law’s analysis frames it as a breakdown in accounting controls, and Reuters reporting via Yahoo Finance notes ADM had to revise its reports twice before the case closed.
The Road to 2027: Continuous Control Monitoring and AI Review
Testing is moving from samples to full populations. When a control runs in a system, analytics can check every transaction instead of 25, and exceptions reach the owner within a day. The ACFE’s finding that proactive data monitoring cut median losses by 53% shows why this matters for fraud controls.
AI tools will change both sides. Attackers use AI to produce convincing requests for bank-detail changes, which raises the likelihood score for payment fraud. Control teams are starting to use AI to read control evidence and flag gaps, and 24% of SOX programs in Protiviti’s poll already use such tools.
Link controls to your wider framework as you automate. The COSO ERM framework and our note on COSO and SOX show how internal control fits enterprise risk management, and the ISO 31000 and COSO comparison helps teams that report under both frameworks.
If your control register lists policies instead of checks, or your ratings have never been tested, we can help you rebuild it around your key risks and the evidence your auditors expect. Read about our risk and internal control services, then book a control library review and we will start with your top ten risks.
Chris Ekai is a Risk Management expert with over 10 years of experience in the field. He has a Master’s(MSc) degree in Risk Management from University of Portsmouth and is a CPA and Finance professional. He currently works as a Content Manager at Risk Publishing, writing about Enterprise Risk Management, Business Continuity Management and Project Management.