Residual risk means the risk that remains after all planned controls and treatments have been applied. It is the inherent risk of an activity minus the reduction the controls deliver, scored on the same scale, and it is the number a manager accepts, transfers, or sends back for more treatment. No control set removes it entirely.
On March 17, 2026, Aura, a Boston-based identity theft protection company, disclosed that an employee had been the target of a phone phishing call and that the caller had used the employee’s account for approximately one hour. In that hour the intruder read about 900,000 records from the company’s systems.
Aura holds ISO/IEC 27001 and SOC 2 Type II certifications, and its core monitoring database, which stores Social Security numbers and financial details, was never touched. The controls did the work they were designed to do. What the attacker reached was a sales and marketing database inherited from Circle Media Labs, a company Aura acquired in 2021.
| What Does Residual Risk Mean: The Bottom Line |
| Residual risk is the risk that remains after risk treatment. ISO 31073:2022 uses exactly that wording, and the NIST glossary defines it as the portion of risk remaining after security measures have been applied. Both definitions assume treatment has happened and the remainder has been measured. |
| On March 17, 2026, identity-protection company Aura disclosed that one employee had been phoned by an attacker and that the caller then held that employee’s account for about one hour. Roughly 900,000 records were read, most of them from a marketing tool belonging to a company Aura bought in 2021. |
| The score is inherent risk minus the effect of controls, expressed on the same scale. A worked 5 x 5 example below takes a customer-data risk from 20 to 4 across three treatments, and shows which of the three moved the score under the appetite line of 6. |
| Someone has to own the remainder. NIST SP 800-37 gives that job to a single authorizing official; ISO/IEC 27001 requires risk owners to approve the residual risk in writing. A register without a named acceptor holds unassigned exposure. |
| Controls fail in testing more often than registers assume. PCAOB inspectors found a Part I.A deficiency in 39% of the audits they reviewed in 2024, and ISACA reports 55% of cybersecurity teams understaffed. Residual scores that assume full control effectiveness are optimistic by design. |
| Re-score on a trigger, not on a calendar. An acquisition, a control test failure, a near miss, or a change of supplier each reopens the number, and the Aura case shows what an unreviewed inherited database costs. |
That database is the residual risk in the story. Fewer than 20,000 active and 15,000 former customers had names, email addresses, home addresses, and phone numbers exposed, SecurityWeek reported. The other rows were marketing contacts from a business absorbed five years earlier, and Have I Been Pwned found most of the emails in earlier breaches.
Every control in Aura’s stack was in place on the day of the call. The exposure that remained sat in an acquired system the register had not scored at the weight of the production database. This article explains what residual risk means in the standards, how to calculate it, and who accepts it.
What Does Residual Risk Mean in the Standards That Define It
Every major standard defines the term the same way and differs only in the word used for treatment. ISO 31073:2022, the vocabulary standard that replaced ISO Guide 73, defines residual risk as risk remaining after risk treatment. ISO 31000:2018 uses that vocabulary throughout its risk treatment clause.
The NIST glossary carries three versions. NIST SP 800-30 and CNSSI 4009 call it the portion of risk remaining after security measures have been applied, and NISTIR 8286 calls it the risk that remains after risk responses have been documented and performed. The second version matters, because documented and performed are two separate tests.
A control written into a policy but not yet operating reduces nothing. A control operating but never tested may reduce less than the register assumes. The risk controls that count toward the residual figure are the ones with evidence of operation, and for that reason the RCSA process tests design and operating effectiveness separately.
| Source | Definition of residual risk | What the wording assumes |
| ISO 31073:2022 (ISO vocabulary) | Risk remaining after risk treatment | Treatment options include retaining the risk; residual risk can contain unidentified risk |
| NIST SP 800-30 Rev. 1 and CNSSI 4009 | Portion of risk remaining after security measures have been applied | Measures are applied, not merely planned; scope is information systems |
| NISTIR 8286 (ERM integration) | Risk that remains after risk responses have been documented and performed | Both a record and evidence of performance exist |
| UNDRR terminology | Disaster risk that remains even when effective disaster risk reduction measures are in place | Emergency and recovery capacity must be maintained for it |
| ISO 14971:2019 (medical devices) | Risk remaining after risk control measures have been implemented | Manufacturer must evaluate and disclose it in the device information |
The five definitions agree on the concept and differ on what counts as treatment. Sources: ISO, NIST CSRC glossary, UNDRR.
The UNDRR definition adds a point the corporate standards leave implicit: residual risk is the reason emergency response and recovery capacity exist at all. If controls removed the risk, no continuity plan would be needed. The ISO 14971 definition adds disclosure, so a device maker must tell users what remains.
Aura’s case fits each of these definitions. The firm had treated the risk to its production data and the treatment held. The marketing database was a second population of records with its own likelihood and its own impact, and the remainder there was larger than the register apparently showed.
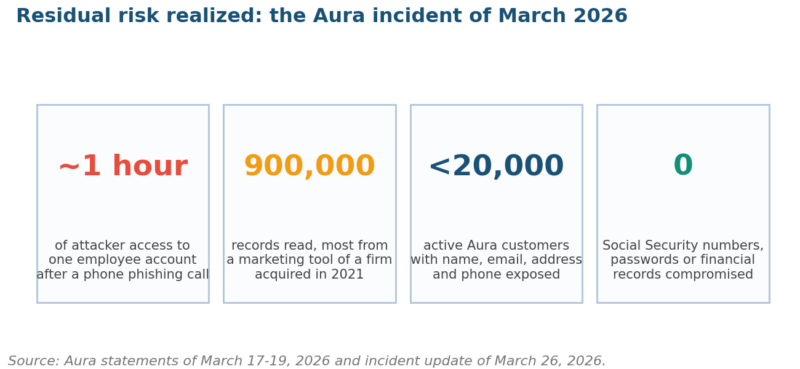
Figure 1. The Aura incident by the numbers. Source: Aura statements of March 17 to 19, 2026 and incident update of March 26, 2026.
Inherent, Secondary, and Accepted Exposure: Keeping the Terms Apart
Residual risk sits in a family of four terms that practitioners mix up in registers and board papers. ISO 31000 does not define inherent risk; the term comes from audit practice and is standard in the COSO ERM framework and in every GRC platform on the market. The ISO 31000 versus COSO comparison explains why the two frameworks diverge here.
The FAIR Institute argues that inherent risk as commonly scored, with no controls at all, describes a state that has never existed. Its recommended alternative is current risk, meaning the exposure with the controls that actually operate today, which is what most registers mean when they write residual.
| Term | Meaning | Where it appears in the register |
| Inherent risk | Exposure before any control is considered; the raw likelihood and impact | The first score, used to rank where controls are needed |
| Current or residual risk | Exposure with the controls that operate and have evidence of operating | The score compared with appetite; the number an owner accepts |
| Target risk | The exposure the plan expects once planned treatments are complete | The forecast column with treatment owner and due date |
| Secondary risk | A new risk created by a treatment, such as a vendor added to transfer the work | A new row, scored on its own, linked to the treatment that created it |
| Accepted risk | Residual risk that a named owner has formally agreed to carry | Sign-off name, date, review date, and the limit above which it must return |
Five terms that share one scale. Inherent, residual, and target sit on the same row; secondary and accepted risk need rows and signatures of their own.
Secondary risk is the one most often missing. Aura’s 2021 acquisition of Circle Media Labs treated a commercial risk and created a data-protection one: a marketing database with roughly 865,000 contacts arrived inside the company’s perimeter. The sibling article on inherent versus residual risk covers the scoring mechanics; this one covers what the remainder means and who signs for it.
Accepted risk needs a limit written beside it, or the acceptance is only a decision to stop looking. A useful register line reads: residual score 6, accepted by the chief information officer on a stated date, review in twelve months, return to committee if the score reaches 9. Our risk appetite statement examples show how those limits are written.
Why the Number That Remains Decides Who Signs and Who Pays
The residual figure is the only risk number that carries a signature, and the signature makes it matter more than the inherent one. NIST SP 800-37 Rev. 2 makes the authorizing official the one person who can accept the security and privacy risk of a federal system, and the authorization decision is a statement that the remaining risk is acceptable.
ISO/IEC 27001 takes the same position for the private sector. Clause 6.1.3 of the 2022 edition requires the risk owners to approve the risk treatment plan and to accept the residual information security risks, and auditors ask to see that approval as a record. A register that stops at treatment recommendations has not finished the clause.
The signer also answers for the loss. IBM’s Cost of a Data Breach Report 2026 puts the global average breach at $4.99 million, a 12% rise on the prior year and a record. That figure is the realized residual risk of the organizations studied, and every one of them had controls in place when the breach began.
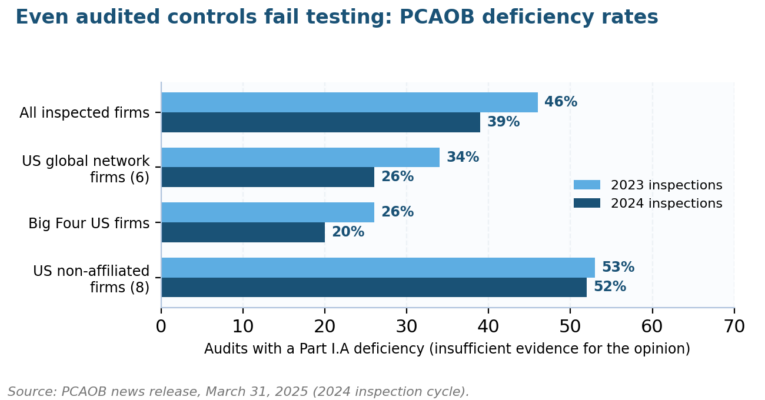
Figure 2. Deficiency rates in PCAOB inspections. Source: PCAOB news release of March 31, 2025, covering the 2024 inspection cycle.
Controls also fail their own tests more often than a register assumes. The PCAOB reported a Part I.A deficiency, meaning the auditor lacked sufficient evidence for its opinion, in 39% of the audits inspected in 2024, down from 46% in 2023. If the profession that tests controls misses evidence that often, a self-assessed rating of fully effective should be discounted.
The residual number therefore drives five decisions that the inherent number cannot. We list them because each one needs a named owner in the risk register and a date beside it, and because the register template we publish carries a column for each.
- Acceptance: whether the owner signs for the remainder as it stands, and at what review interval
- Treatment budget: which risks above appetite receive the next control dollar, ranked by residual score, since the inherent score only shows where controls already exist
- Transfer: whether insurance or contract terms are worth buying for the remaining severity, and at what deductible
- Continuity planning: which residual scenarios need a tested recovery plan because the remaining likelihood is above zero
- Disclosure: what regulators, customers, or device users must be told about the exposure that stays
Boards read residual scores as a promise. When a heat map shows a risk inside appetite, directors assume the controls named beside it operate and were tested. The evidence column exists to back that assumption, and risk appetite, tolerance, and capacity must be set before the map is drawn.
How to Calculate Residual Risk with a 5 x 5 Worked Example
The formula is simple and the inputs are not. Residual risk equals inherent risk minus the reduction delivered by the controls, and on a qualitative 5 x 5 matrix the arithmetic is done by re-scoring likelihood and impact after each control instead of subtracting a percentage from the inherent score.
Take a risk shaped like Aura’s: an attacker reaches customer contact data through a staff account and a legacy database. Inherent likelihood scores 5, because ISACA’s 2025 survey names social engineering as the top attack type for 44% of respondents, and inherent impact scores 4 for a regulated notification event, giving an inherent score of 20.
| Treatment step | Likelihood | Impact | Score | Why the number moved |
| Inherent, no controls counted | 5 | 4 | 20 | Phone phishing is common and the data is regulated |
| Phishing-resistant MFA plus quarterly access review | 4 | 3 | 12 | Session hijack still possible; access review limits what one account can reach |
| Purge or segregate the acquired marketing database | 2 | 3 | 6 | The largest population of records is no longer reachable from a staff account |
| Cyber insurance with notification cover | 2 | 2 | 4 | Likelihood unchanged; the cost of the notification event is transferred |
| Target after the annual control test | 2 | 2 | 4 | Held only if the MFA and purge controls pass their operating tests |
Worked scoring for a customer-data risk. Appetite ceiling set at 6; the second treatment is the one that brought the score inside it.
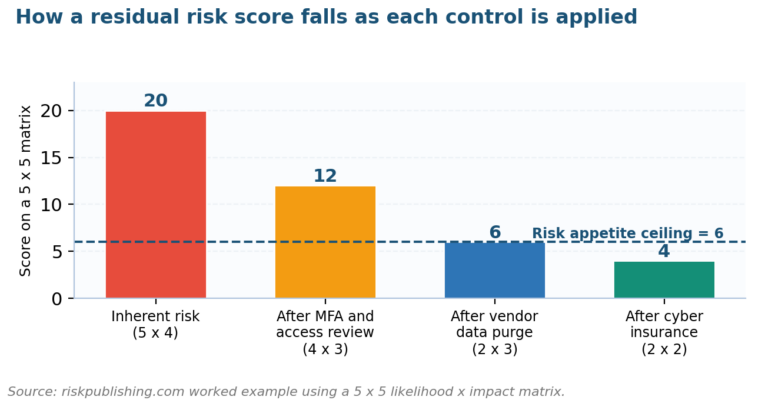
Figure 3. The same worked example as a chart. Source: riskpublishing.com scoring on a 5 x 5 likelihood by impact matrix.
We apply four rules when reviewing this arithmetic in client registers, and they hold for a quantitative model as much as for a matrix. They are the rules most often skipped when a team is scoring two hundred rows in an afternoon workshop with the auditor due the following week.
- Score only controls with evidence of operation in the period; a planned control moves the target column, never the residual column
- Move likelihood and impact separately and write down why, because a control that transfers cost changes impact and leaves likelihood alone
- Apply a discount to self-assessed effectiveness until an independent test confirms it, following the operating-effectiveness step in the RCSA
- Re-score any row whose control failed a test, whose owner changed, or whose scope grew through an acquisition or a new supplier
Quantitative programs do the same arithmetic in dollars. A FAIR-based cyber risk quantification gives an annualized loss expectancy before and after controls, and the residual figure is the after number. The choice between scales is covered in qualitative versus quantitative assessment, and the inherent risk score in Excel walkthrough builds the first column.
Treatment Options After the Controls Are In: Accept, Reduce, Transfer, Avoid
Once the residual score is known, ISO 31000 clause 6.5 lists the options: avoid the activity, take more risk to pursue an opportunity, remove the source, change likelihood, change consequences, share the risk, or retain it by informed decision. In practice the register uses four of them.
| Option | When it fits the residual score | Register evidence required |
| Accept | Score at or below appetite, and the cost of the next control exceeds the reduction it buys | Owner’s signature, date, review date, and the trigger score for return |
| Reduce | Score above appetite and a control exists whose cost is below the expected loss avoided | Control owner, due date, target score, and the test that will confirm operation |
| Transfer | Impact is severe, likelihood is low, and a counterparty prices the loss below the internal cost | Policy or contract reference, limits, exclusions, and the secondary risk row for the counterparty |
| Avoid | No affordable control brings the score inside appetite and the activity is not essential | Decision record, the activity withdrawn, and the date the row is closed |
The four working options after treatment. ISO 31000 lists seven; retention and sharing are the two most often recorded without evidence.
Transfer has one trap. Insurance changes the impact column and leaves likelihood where it was, so a transferred risk still happens at the same rate; the Allianz Risk Barometer 2026 ranks cyber incidents as the top business risk for the fifth year, at 42% of responses, and insurers price that. The risk response planning guide covers the contract terms.
Acceptance goes wrong most often, because it is the cheapest option to record. The tolerance limits in the appetite statement decide the score at which acceptance is allowed, and mitigation planning decides what happens when the score sits above them. A residual risk accepted above tolerance with no escalation record will be written up at the next audit.
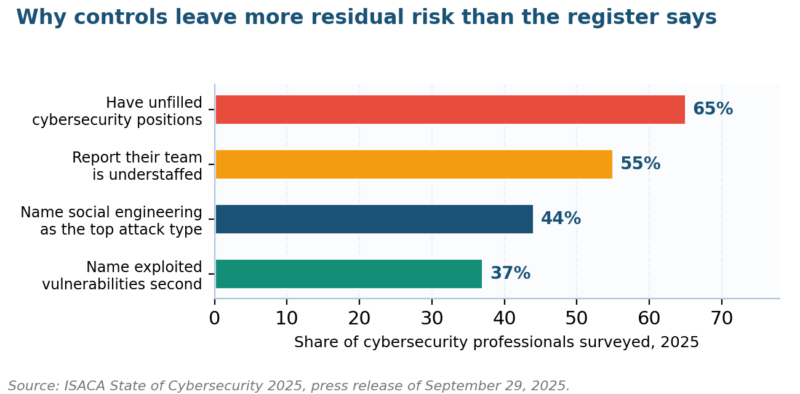
Figure 4. Staffing and attack pressures that widen the gap between designed and operating controls. Source: ISACA State of Cybersecurity 2025.
Those staffing numbers explain why residual scores drift upward between reviews. ISACA reports that 65% of organizations have unfilled cybersecurity positions and 55% describe their teams as understaffed. A control designed for a fully staffed team operates below its designed strength, and the residual figure should say so.
The re-score triggers below belong in the written register procedure, where an auditor can find them and a new risk owner can follow them without briefing. The update frequency guide explains how each one is logged, who raises it, and how long the row may stay open before the committee sees it.
- A control fails its operating test, or the test is missed for a period
- An acquisition, migration, or new supplier brings records or systems inside the perimeter
- A near miss or incident touches the risk, in the organization or in a peer’s public disclosure
- The owner, the appetite statement, or the regulatory requirement behind the row changes
Worked Examples Across Cyber, Safety, Finance, and Healthcare
The concept is the same in every field, and the evidence for it differs. The examples below use public cases and standards so a reader can check the residual figure against a source, and each row names the control that was operating when the risk assessment was last signed.
| Field | Controls in place | What remained | Standard that names it |
| Cyber (Aura, 2026) | ISO 27001 and SOC 2 programs, segregated production database, incident response plan | An acquired marketing database reachable from one staff account; 900,000 records read in an hour | NISTIR 8286: risk after responses are documented and performed |
| Aviation (DCA, 2025) | Charted helicopter routes, tower separation, collision-avoidance systems | 67 deaths when routes, workload, and altitude errors combined; NTSB found the FAA never assessed the route’s risk | NTSB final report of January 28, 2026 |
| Safety (OSHA hierarchy) | Elimination, substitution, engineering and administrative controls, PPE | Exposure that PPE and procedures reduce but cannot remove; the reason permits and rescue plans exist | OSHA hazard prevention and control guidance |
| Financial reporting | Internal control over financial reporting, external audit | 39% of inspected audits in 2024 lacked sufficient evidence for the opinion | PCAOB inspection reports, Part I.A |
| Medical devices | Design controls, protective measures, labeling | Risk the manufacturer must evaluate and disclose after all controls | ISO 14971:2019 residual risk evaluation |
Residual exposure in five fields. Each row names the controls that were operating and the remainder that a source documented afterward.
The aviation row shows a remainder nobody scored. The NTSB’s final report on the January 29, 2025 collision over the Potomac found that the FAA lacked effective strategies to identify, assess, and reduce recurring midair collision hazards around Reagan National, despite data showing repeated close encounters. The controls existed; the residual risk of the combination was never scored.
The safety row is where the concept was first made operational. OSHA’s hazard prevention and control guidance orders controls from elimination down to personal protective equipment, and everything below elimination leaves a remainder. A bow-tie analysis draws that remainder as the paths that pass every barrier.
Third-party risk is where residual scores are most often wrong, because the controls belong to someone else. A third-party risk management framework scores the supplier’s controls on the supplier’s evidence, and the Aura acquisition shows why an inherited system needs the same identification pass as a new one.
Where Reporting of the Remaining Exposure Goes Wrong
The mistakes below recur in the registers we review, in banks, pension funds, and public bodies alike. Each has a fix that costs a column or a signature and needs no new system, and the first four account for most of the gap between reported and actual exposure.
| Failure | How it shows up | Fix |
| Planned controls scored as operating | Residual score drops the day the control is approved, not the day it runs | Separate residual and target columns; move a score only on evidence of operation |
| Self-assessed effectiveness taken at face value | Every control rated fully effective; no test dates in the register | Discount untested controls one level; schedule operating tests through the RCSA cycle |
| No named acceptor | Residual scores inside appetite with nobody’s signature beside them | Add owner, date, and review date; treat an unsigned score as unaccepted |
| Inherited scope never re-scored | Acquired systems and legacy databases carry the parent’s score or none | Run identification and scoring on every acquired asset within 90 days of close |
| Transfer recorded as reduction | Insurance shown as lowering likelihood | Move impact only; add the insurer as a secondary risk row with limits and exclusions |
| Acceptance above tolerance without escalation | Scores of 9 or higher accepted at manager level | Set the escalation score in the appetite statement; log the committee decision |
| Register reviewed on a calendar only | Annual update while control failures and incidents go unlogged | Adopt the trigger list; a failed test or near miss reopens the row the same week |
Seven register failures and their fixes, drawn from RCSA reviews in financial services and the public sector.
The most expensive failure on that list is reporting inherent scores to the board because they look more urgent. Directors then fund controls that already exist and miss the residual rows above appetite. The KPI dashboard guide shows a layout that reports both columns and the gap between them.
The second is treating the five-step process as finished at treatment. Monitoring and review is the step that keeps the residual figure true, and the risk management techniques that belong there are testing, indicator tracking, and incident reconciliation, none of which happen in a scoring workshop.
What Does Residual Risk Mean: Your Questions Answered
What is residual risk in simple terms?
Residual risk is the risk that is still there after you have done everything you planned to do about it. ISO 31073:2022 defines it as risk remaining after risk treatment, and NIST calls it the portion of risk remaining after security measures have been applied. It is the number someone must accept.
What is the residual risk formula?
Residual risk equals inherent risk minus the reduction delivered by controls, on the same scale. On a 5 x 5 matrix, re-score likelihood and impact after each operating control and multiply; in a quantitative model, subtract the loss the controls avoid from the annualized loss expectancy. Count only controls with evidence of operation.
What is the difference between inherent risk and residual risk?
Inherent risk is the exposure before any control is counted; residual risk is the exposure with the controls that operate today. The inherent score decides where controls are needed, and the residual score decides what an owner accepts. Both belong on the same register row with the control evidence between them.
Can residual risk ever be zero?
No, except by avoiding the activity altogether, which closes the row rather than reducing it. Every control below elimination leaves a remainder, and the ISO 31073 note adds that residual risk can include unidentified risk. Aura’s certified control program still left a legacy database that an hour of access exposed.
Who is responsible for accepting residual risk?
A named owner with the authority to bear the loss. NIST SP 800-37 assigns that role to a single authorizing official for each federal system, and ISO/IEC 27001 clause 6.1.3 requires risk owners to approve the treatment plan and accept the residual risks. Acceptance is recorded with a date, a review date, and an escalation score.
How often should residual risk be reviewed?
On every trigger and at least once a year. Triggers include a failed control test, an incident or near miss, an acquisition or new supplier, and a change of owner or appetite. The Aura database sat unreviewed for five years after the 2021 acquisition, which is the case for trigger-based review over calendar review.
How does residual risk affect insurance decisions?
It sets the severity worth insuring. Insurance transfers the cost of the remaining impact and leaves likelihood unchanged, so the decision compares the premium against the residual impact multiplied by the residual likelihood. Cyber incidents lead the Allianz Risk Barometer 2026 at 42% of responses, and premiums reflect that residual frequency.
Where the Profession Is Heading After the Controls Are Counted
Acquired systems will be the residual rows that decide the next five years of disclosures. Every acquisition brings databases, accounts, and suppliers that were scored, if at all, by a different team against a different appetite, and the Aura case shows the cost of leaving that scoring for later.
Set a 90-day rule now: every asset that arrives through an acquisition, migration, or new supplier gets an identification pass and a residual score before the integration is called complete. Write the rule into the appetite statement so the deal team cannot waive it, and give the register owner the right to hold the integration sign-off.
Control testing is moving from annual samples to continuous evidence. Identity platforms log every authentication, access reviews can run on a schedule, and the operating evidence that an RCSA once collected by interview arrives as data. Residual scores can then move on the day a control fails, months ahead of the next workshop.
Regulators are asking for the signature. Federal authorizing officials already sign for residual risk under SP 800-37, ISO/IEC 27001 auditors ask for the owner’s acceptance record, and boards are adopting the same test for enterprise rows. A residual score without a named acceptor will read as an open finding.
Registers come to us with inherent scores, planned controls, and no acceptance column. We rebuild the residual column against ISO 31000 and the operating evidence, set the escalation scores, and hand back a register a board can sign. The services page describes the formats, and the contact page is where to send the register.
Chris Ekai is a Risk Management expert with over 10 years of experience in the field. He has a Master’s(MSc) degree in Risk Management from University of Portsmouth and is a CPA and Finance professional. He currently works as a Content Manager at Risk Publishing, writing about Enterprise Risk Management, Business Continuity Management and Project Management.